Table Of Content
Related Posts
DLP at 50, 250, and 1,000 Employees: How the Right Answer Changes as You Grow
-
September 16, 2026
-
Quick Answer:
AI Security Posture Management (AISPM), also called AI Posture Management, is the continuous process of discovering, monitoring, and controlling how AI tools, models, and agents interact with your company's data and systems. It covers everything from spotting an unapproved AI app on someone's laptop to blocking a customer record from being pasted into a public chatbot. Most teams that manage AI posture well pair a discovery layer with policy enforcement at the point where employees actually use AI, which is the endpoint.
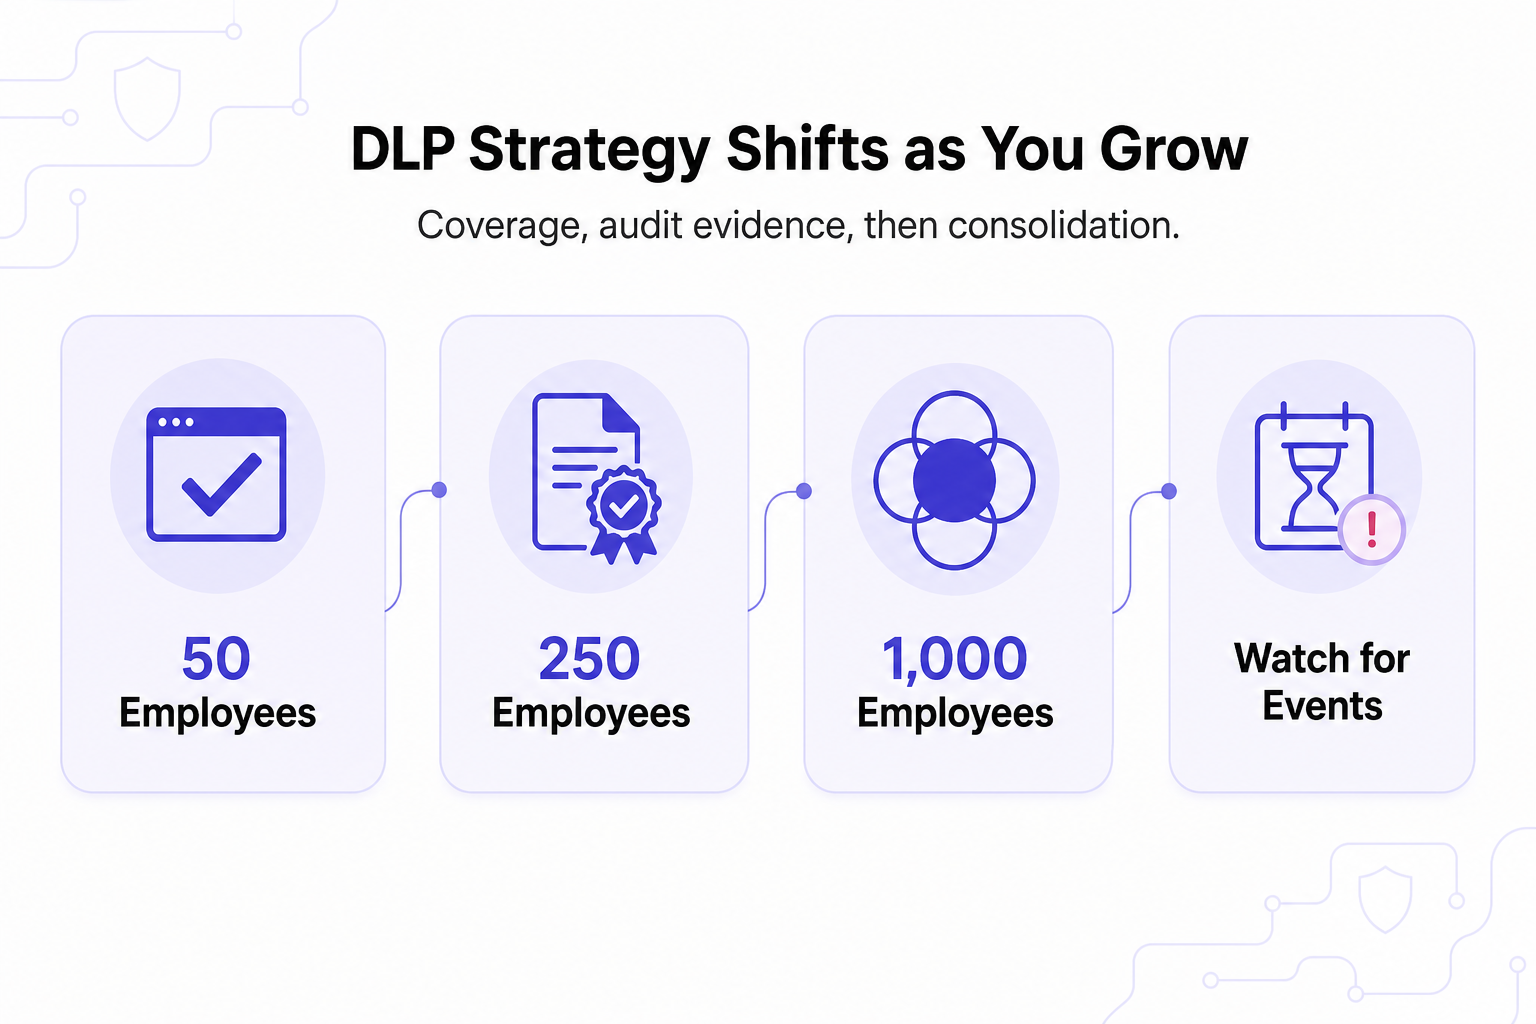
Data loss prevention is not a single product decision made once. The right data loss prevention strategy at 50 employees looks almost nothing like the right strategy at 1,000, because the trigger changes: at 50 it is coverage without a security hire, at 250 it is passing your first audit, and at 1,000 it is stopping tool sprawl from breaking your own policy. Companies that pick a DLP approach based on their current headcount, and revisit it as they cross each threshold, avoid both the under-protection of doing nothing and the over-engineering of buying enterprise tooling before there is anyone to run it.
TL;DR
- At 50 employees, nobody owns security full time. The requirement is broad coverage that runs itself, not a console that needs daily attention.
- At 250 employees, the first serious compliance audit shows up. The requirement shifts to evidence a third-party auditor will accept, not just internal peace of mind.
- At 1,000 employees, tool sprawl becomes the actual risk. The requirement becomes consolidation: one policy enforced consistently, not five overlapping tools each enforcing a slice of it.
- Watch for migration signals, not calendar dates. Headcount is a proxy; the real trigger is a new hire, a new customer contract, or a new audit request.
- GenAI has compressed the timeline for all three bands. Shadow AI usage and copilot-driven data movement now show up in companies far smaller than the ones that traditionally worried about DLP.
About the author: This article is written from Kitecyber’s experience deploying endpoint-native DLP across mid-market and regulated companies, from 50-person fintech startups preparing for their first SOC 2 audit to 1,000-plus employee organizations consolidating point tools into a single policy. Kitecyber’s customer base, including companies like Scrut Automation and Sarvam, spans exactly this growth curve.
What Changes at 50 Employees?
At 50 employees, the defining fact is not the size of the data footprint, it is the absence of anyone whose job is security. Most companies at this stage have a founder, a head of engineering, or an IT generalist handling security as one of several responsibilities, not a dedicated analyst reviewing alerts. This is also the point where several employment and reporting thresholds start to apply to the business more broadly, which tends to be the same moment leadership starts asking what data protection actually covers.
The requirement at this stage is coverage with near-zero operating burden. That means:
- Deployment that does not require a project plan. If turning on DLP takes a two-week rollout with professional services, it will get deprioritized behind product and sales work.
- Default policies that catch the obvious risks (customer records, source code, credentials leaving through email, USB, or a browser upload) without weeks of tuning.
- Alerting that a generalist can act on. A queue of a few clear, high-confidence incidents beats a hundred low-confidence ones.
What typically goes wrong at 50 is one of two failure modes. Either the company does nothing, reasoning that DLP is for bigger companies, and only notices a data movement policy gap after a customer asks about it during a security questionnaire. Or the company buys a legacy DLP suite designed for enterprise security operations centers, and the tool ends up half-configured because nobody has the bandwidth to run it properly. A DLP tool that requires a dedicated analyst to be effective is, functionally, not deployed at a 50-person company. The right answer here is a data loss prevention tool that runs close to default-safe out of the box and gets more precise as it observes real usage, not one that assumes a trained operator is watching it every day.
What Changes at 250 Employees?
Building on the coverage question above, a different trigger appears around 250 employees: the first serious compliance audit. This is usually driven by a customer contract, an investor requirement, or a regulatory obligation, and it changes DLP from an internal safeguard into something a third party has to independently verify. SOC 2 is a voluntary, customer-driven framework rather than a size-based legal requirement, so it can appear earlier or later than 250 depending on your customer base. That headcount range is also where GDPR Article 30’s record-keeping obligations become hard to avoid — its under-250-employee exemption falls away for processing that isn’t occasional, carries risk to individuals, or involves special-category data, which covers most companies handling customer or health records. Regulatory frameworks like GDPR and HIPAA apply based on the type of data an organization processes, not its size, so a 60-person healthcare startup handling protected health information already carries HIPAA obligations well before it hits 250 employees.
The requirement at this stage shifts from “we have some protection” to evidence an auditor will accept. That is a meaningfully different bar:
- Logs that show what happened, not just that a policy exists. An auditor wants proof of enforcement, not a policy document.
- Data lineage tracking that can answer where a specific piece of sensitive data went, who touched it, and what action was taken, across endpoints, SaaS apps, and now GenAI tools.
- Consistent classification. If your data classification software tags a customer list as sensitive in one system and misses it in another, the audit will surface the gap.
What typically goes wrong at 250 is treating the audit as a paperwork exercise instead of a controls exercise. Teams write policies that describe intended behavior, then discover during the audit that the DLP tooling in place cannot actually produce evidence of that behavior. A related failure: adopting generative AI tools for productivity without adding any control over what leaves through them. In a November 2024 Capgemini Research Institute survey of large organizations (all with revenue over $1 billion), 97% reported security incidents or breaches linked to generative AI. LayerX Security’s 2025 research found that while roughly 45% of employees use GenAI tools, 77% of those users paste data into them — and about a fifth of those pastes contain sensitive PII or payment data, frequently from unmanaged personal accounts. IBM’s Cost of a Data Breach Report 2025 separately found that 20% of organizations suffered a breach tied to unsanctioned shadow AI. None of that shows up in a policy document; it shows up in an audit finding when nobody has visibility into shadow AI usage. An endpoint-native DLP agent that also covers SaaS app protection and web gateway controls, because the same agent extends beyond pure DLP, tends to help address more SOC 2 and ISO 27001 controls in one pass than a point DLP product checked against the same evidence request, though certification still depends on how the organization configures, operates, and documents its program.
What Changes at 1,000 Employees?
A related but distinct question emerges once a company crosses roughly 1,000 employees: the problem stops being coverage or evidence and becomes sprawl. By this size, most organizations already have several overlapping tools built around their DLP needs, from a legacy suite from an earlier acquisition to adjacent tools layered on for web filtering, device management, or a specific SaaS app. Each one enforces its own slice of policy, often with its own definition of what counts as sensitive.
The requirement at this stage is consolidation and unified policy, not more tools. Specifically:
- One policy definition enforced consistently across endpoints, cloud apps, email, and browser, rather than five separate policy engines that drift out of sync over time.
- Enterprise DLP solutions that cover Windows, macOS, native Linux, and mobile from a single agent, so engineering and IT do not maintain a different tool per operating system.
- Visibility into agentic workflows. At this scale, autonomous AI agents are frequently running on company devices, reading and moving data on their own schedule, and legacy tools built around static regex patterns and human-speed traffic inspection were not designed to see that.
What typically goes wrong at 1,000 employees is treating consolidation as a simple subtraction problem, ripping out old tools without first mapping which control each one was actually satisfying for which auditor or customer. The other common failure is adding a new point solution for each new problem (one tool for shadow AI detection, another for insider risk, another for removable media) which recreates the exact sprawl the company was trying to escape. Because endpoint-native DLP already includes context-aware classification, real-time enforcement, and native GenAI security, it tends to absorb these needs into the existing agent rather than adding another console to monitor.
What Are the Signals You Have Outgrown a Band?
Stepping back from headcount as the trigger, the more reliable signals are events, not dates. You have outgrown the 50-employee posture when a customer’s security questionnaire asks for specifics your current tooling cannot answer, or when you make your first dedicated security or IT hire. You have outgrown the 250-employee posture when a second or third framework (ISO 27001 alongside SOC 2, or HIPAA alongside PCI DSS) enters the picture and your evidence has to serve multiple auditors at once. You have outgrown the 1,000-employee posture when a security review takes longer because engineers have to check three different consoles to answer one question about where a file went.
About Kitecyber
Kitecyber is a data loss prevention (DLP) platform built for the GenAI era, delivered as one lightweight agent. It operates on a continuous See, Decide, Enforce model: discovering sensitive data across endpoints, SaaS and cloud apps, email, browser, clipboard, and removable media with context-aware classification, tracking its movement in real time, and enforcing the right action, allow, block, warn, coach, log, or isolate, at the exact point of risk. Because the same agent extends beyond pure DLP to also cover SaaS app protection and web gateway controls, it helps address more SOC 2, ISO 27001, HIPAA, and PCI DSS controls in one pass than a point DLP product, without deploying anything extra. Kitecyber serves growth-stage and regulated companies, including fintech, healthcare, insurance, and GenAI-native businesses, that need enterprise-grade data protection without an enterprise-sized security team.
To learn how an endpoint-native DLP approach scales from your first audit to consolidation at scale, start a trial at Kitecyber.
See verified customer reviews of Kitecyber on G2 and SourceForge.
To learn how an endpoint-native DLP approach scales from your first audit to consolidation at scale, start a trial at Kitecyber.
See verified customer reviews of Kitecyber on G2 and SourceForge.
References
Frequently Asked Questions
No. Frameworks like GDPR and HIPAA apply based on the type of data processed, not company size. GDPR Article 30 has an under-250-employee exemption for its records-of-processing duty, but that exemption falls away for processing that isn't occasional, carries risk to individuals, or involves special-category data — so many smaller organizations still owe those records.
No. SOC 2 is a voluntary, customer-driven framework, typically requested by enterprise customers or investors rather than triggered automatically by headcount.
Yes, and increasingly earlier than expected. LayerX Security's 2025 research found that among employees who use GenAI tools, 77% paste data into them — often from unmanaged personal accounts outside any enterprise oversight — so shadow AI detection matters even before an audit forces the question.
Not necessarily. The requirement changes at each band, but a tool built to scale in configuration and coverage, rather than one built only for a single stage, can often adapt without a full replacement.
Data lineage tracking records where a specific piece of sensitive data traveled, who accessed it, and what action was taken at each point, which is the specific form of evidence auditors request beyond a policy statement.
It compresses the timeline. Copilots and autonomous agents can read and move data at machine speed, so even a 50-person company now faces the kind of exfiltration risk that used to be associated only with much larger organizations.
Adding a new point product for each new risk category, such as one tool for insider risk and a separate one for removable media, instead of extending a single agent's policy to cover the new risk.
Ajay Gulati
Ajay Gulati is a passionate entrepreneur focused on bringing innovative products to market that solve real-world problems with high impact. He is highly skilled in building and leading effective software development teams, driving success through strong leadership and technical expertise. With deep knowledge across multiple domains, including virtualization, networking, storage, cloud environments, and on-premises systems, he excels in product development and troubleshooting. His experience spans global development environments, working across multiple geographies. As the co-founder of Kitecyber, he is dedicated to advancing AI-driven security solutions.