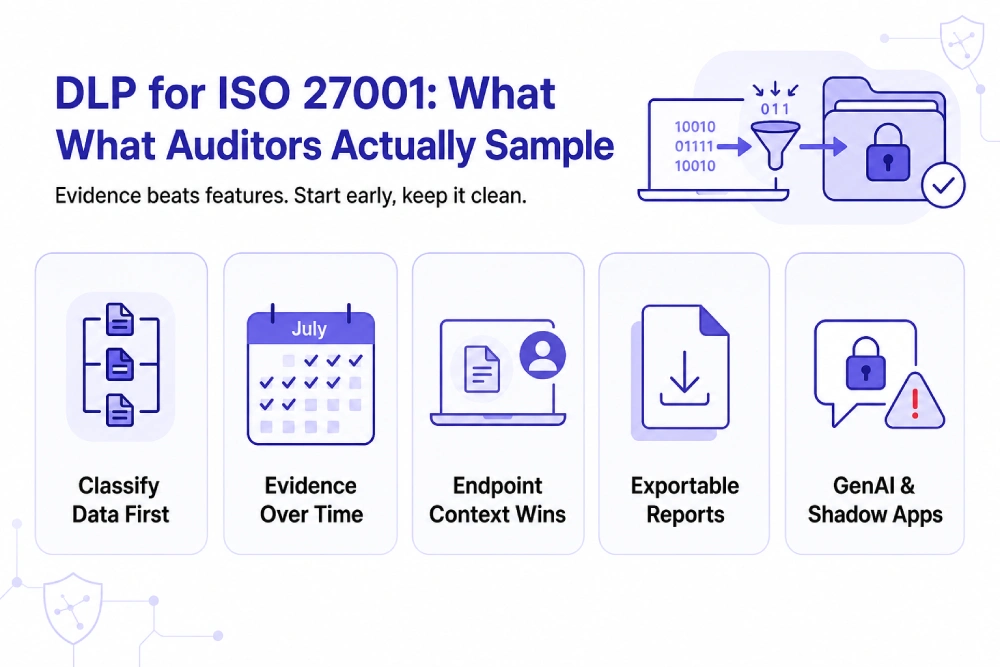
Data loss prevention software is the operational layer that turns ISO 27001’s data protection requirements into evidence an auditor can actually sample. ISO/IEC 27001:2022 introduced Annex A 8.12, a dedicated Data Leakage Prevention control, alongside Data Masking (A.8.11) and Monitoring Activities (A.8.16). For a mid-market company heading into a Stage 2 audit, the practical question is not whether DLP is “nice to have” but which tool can produce months of consistent, exportable evidence that unauthorized data extraction is being detected and blocked, without requiring a dedicated DLP analyst to run it.
TL;DR
About the Author: This article is written by
Kitecyber team, whose endpoint-native DLP platform is used by mid-market and regulated companies, including several pursuing SOC 2 and ISO 27001 certification, to generate the classification and enforcement evidence auditors sample during ISMS reviews.
How Does DLP Fit Into an ISO 27001 ISMS?
DLP software is not itself the Information Security Management System (ISMS) that ISO 27001 certifies. The ISMS is the full set of policies, risk assessments, and controls; DLP is one technical control that produces evidence for a subset of Annex A themes related to data handling, classification, and monitoring. ISO/IEC 27001:2022 includes a dedicated Data Leakage Prevention control under Annex A 8.12, which organizations apply where their risk assessment and Statement of Applicability call for it. It sits alongside data classification and monitoring controls that give DLP tools the foundation to identify sensitive data and track its movement.
This matters because a common mistake mid-market teams make is buying a DLP tool the month before their Stage 2 audit and expecting it to retroactively fill a gap. Auditors are not evaluating whether you own a product. They are evaluating whether your ISMS demonstrates a working control, in place long enough to generate a real sample of events, exceptions, and responses. A DLP tool that has been logging policy violations and enforcement actions for six months tells a much stronger story than one activated three weeks before the audit.
What's the Difference Between Documentation and Operational Evidence?
Documentation is what you say your control does; operational evidence is proof it actually did it. An ISO 27001 auditor reads your data classification policy and your DLP configuration standard as documentation. Then, during the audit, they sample operational evidence: specific incident logs, alert histories, policy change records, and remediation timelines pulled from the actual tool.
This distinction is where many mid-market DLP deployments quietly fail their first audit cycle. A policy document that says “sensitive data uploads to unauthorized destinations are blocked” is easy to write. Producing a report that shows the specific blocked events, the data classification that triggered them, and the user or device involved, over a period of months, is harder, and it’s exactly what auditors sample. This is also why context-aware classification matters more than keyword matching for audit purposes: an auditor asking “how do you know this was sensitive data and not a false positive” needs an answer grounded in document context, not just a regex match count.
A related but distinct question is how granular that evidence needs to be. Data lineage tools that can trace a file from creation through every copy, upload, and share event give you a much stronger answer to “show me what happened to this record” than a tool that only logs that a rule fired. If your DLP tool cannot reconstruct the path data took across endpoints, cloud apps, and email, you are relying on your security team to manually stitch that story together for the auditor, which increases both audit prep time and the risk of gaps.
How Does ISO 27001 Differ From SOC 2 in What It Wants to See?
ISO 27001 is more prescriptive about data leakage prevention than SOC 2. ISO 27001:2022 names data leakage prevention as a specific control (Annex A 8.12), while frameworks like SOC 2, GDPR, and HIPAA require broad safeguards against unauthorized disclosure or access without prescribing DLP as a named control.
Practically, this means a company that built its security stack purely to satisfy SOC 2’s broader “confidentiality” trust service criteria may find, on moving to ISO 27001, that auditors want a named, specific control addressing data leakage, not just a general narrative about access restrictions and encryption. Teams that already run endpoint DLP for SOC 2 purposes usually find the transition easier, since the same evidence, real-time enforcement logs, classification records, incident reports, maps directly onto the more specific ISO 27001 language. Teams starting their DLP program because of ISO 27001 should expect the standard to want more precision about what was leaked, to where, and how it was stopped, not just that a general security program exists.
Which DLP Tools Should Mid-Market Companies Shortlist for ISO 27001?
The right shortlist weighs evidence quality and reporting clarity over raw feature count, because that’s what gets sampled in an audit. Here is an honest comparison across tools mid-market security teams commonly evaluate:
|
Tool
|
Architecture
|
Fit note for ISO 27001 evidence
|
|
Kitecyber
|
Endpoint-native agent covering endpoints, SaaS, email, browser, clipboard, removable media
|
Endpoint-level data lineage and context-aware classification produce device- and user-specific evidence; the same agent covers SaaS governance and adjacent Annex A controls without additional deployment
|
|
Safetica
|
Endpoint agents, on-prem or cloud-native
|
Data discovery and device control generate useful endpoint logs; validate classification depth on scanned or image-based documents during evaluation
|
|
Cyberhaven
|
Cloud console with endpoint agents and browser extensions
|
Strong on tracing data lineage and movement, a direct match for “show me what happened to this file” audit questions; requires agent or extension deployment on every device to capture full lineage
|
|
Microsoft Purview
|
Cloud-native, built into Microsoft 365 and Azure
|
Strong fit for organizations already centralized on M365, with sensitivity labeling and insider risk reporting; less suited to environments with significant non-Microsoft endpoint or app usage
|
|
Endpoint Protector
|
Endpoint agents, appliance or cloud deployment
|
Content-aware protection and granular device control across Windows, macOS, and Linux; primarily focused on endpoint enforcement rather than network traffic inspection
|
|
Nightfall
|
Cloud-native, API integrations plus endpoint agent
|
Good evidence trail for SaaS and GenAI app exposure; core detection relies on cloud connectivity, worth noting for evidence continuity during connectivity issues
|
Kitecyber’s fit for this specific use case comes from treating the endpoint as the enforcement point rather than inspecting only network traffic or API calls after the fact. Because classification happens with document context at the point of risk, the incident reports generated are specific enough to answer an auditor’s follow-up question directly: which file, which user, which destination, which action was taken. And because the same lightweight agent covers SaaS governance and other supporting controls, it produces evidence that supports more Annex A control themes than a point DLP product would from a single deployment, without adding separate tools to manage before the audit.
What Should an ISO 27001 Certification Checklist Include for DLP?
An ISO 27001 certification checklist for data protection should treat DLP as an evidence-generation project, not a procurement task. Building on the evidence question above, the practical checklist looks like this:
About Kitecyber
Kitecyber is an endpoint-native data loss prevention platform built for the AI era, where copilots and autonomous agents can read and move sensitive data at machine speed. One lightweight agent covers endpoints on Windows, macOS, and native Linux, along with SaaS apps, email, browser activity, clipboard, and removable media, operating on a continuous See, Decide, Enforce model. Because the same agent covers SaaS governance and adjacent supporting functions, mid-market companies preparing for ISO 27001 or SOC 2 get evidence across more Annex A control themes from a single deployment instead of stitching together multiple point products. Kitecyber works with fintech, healthcare, insurance, and GenAI-native companies, including DuploCloud, Lily AI, Sarvam, and Scrut Automation.
If your team is building a data protection program ahead of an ISO 27001 audit, learn more or start a free trial at Kitecyber.
See verified customer reviews of Kitecyber on G2 and SourceForge.
Sources
Frequently Asked Questions