Table Of Content
Related Posts
Best DLP Platforms for Mid-Market SaaS Companies Protecting Customer Data and Source Code
-
September 16, 2026
-
Quick Answer:
AI Security Posture Management (AISPM), also called AI Posture Management, is the continuous process of discovering, monitoring, and controlling how AI tools, models, and agents interact with your company's data and systems. It covers everything from spotting an unapproved AI app on someone's laptop to blocking a customer record from being pasted into a public chatbot. Most teams that manage AI posture well pair a discovery layer with policy enforcement at the point where employees actually use AI, which is the endpoint.
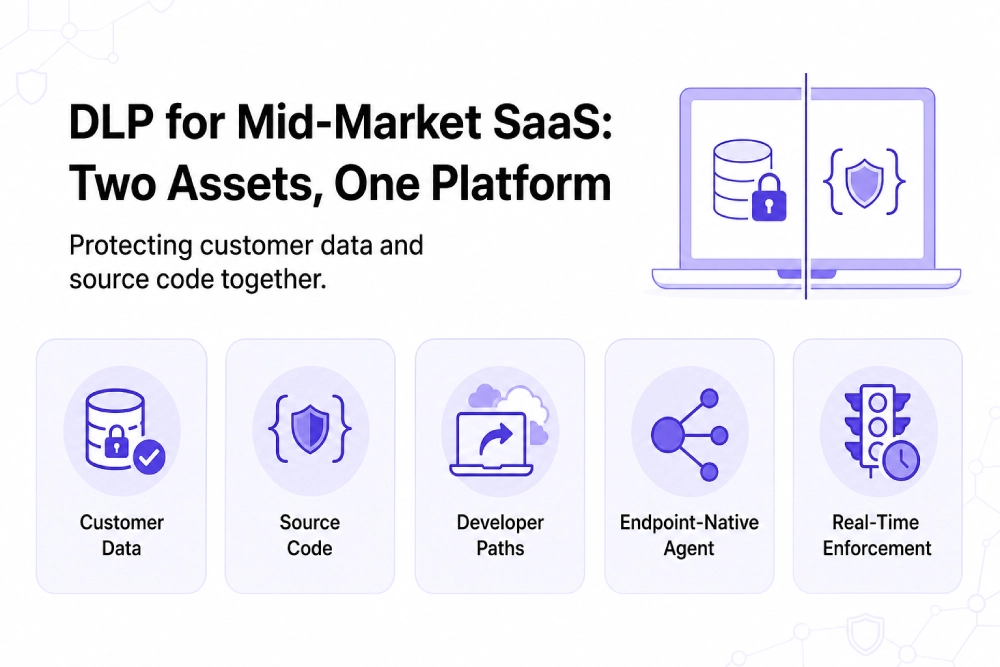
Mid-market SaaS companies, roughly 100 to 1,000 employees, are protecting two fundamentally different assets with the same headcount and budget that a much larger enterprise would dedicate to one: customer data held under contract and regulation, and source code that is the company’s entire competitive advantage. Data loss prevention software built for one of these assets often fails the other, because customer data leaks through app misconfigurations and careless sharing, while source code leaks through a developer’s own daily tools: a git clone to a personal laptop, an AI coding assistant, a package registry, or a pasted snippet in a support ticket. The best DLP platforms for this segment are endpoint DLP solutions that cover both data types natively, including Linux developer workstations, without requiring a security team to build two separate programs.
TL;DR
- Customer data and source code require different controls: one is governed by contracts and regulation, the other by competitive exposure and developer workflow.
- Generic cloud DLP solutions built for SaaS app monitoring frequently miss the developer-specific paths where source code actually leaves: local clones, AI coding assistants, personal package registries, and pasted code in tickets.
- Customer security questionnaires (SOC 2, vendor risk assessments) turn DLP gaps into a sales blocker, not just a security issue.
- Endpoint-native platforms with real Linux support close the gap that agentless, API-only, or Windows/macOS-first tools leave open.
- No DLP platform, including Kitecyber, can claim to stop all source-code exfiltration; the realistic goal is reducing the number of ungoverned paths to as close to zero as operationally possible.
About the Author: This article is written by the Kitecyber team, whose endpoint-native DLP platform is used by illustrative GenAI-native and mid-market SaaS companies, including DuploCloud, Sarvam, Codvo AI, and Scrut Automation, to protect customer data and source code across Windows, macOS, and native Linux endpoints.
Why Do Customer Data and Source Code Need Different DLP Controls?
Customer data and source code fail for different reasons, and a DLP program that treats them identically will under-protect at least one. Customer data, personally identifiable information, payment details, health records, is governed by contracts (your customers’ security addenda), by regulation, and by frameworks your customers audit you against. The controls that matter are access governance, encryption, retention, and provable handling: who touched a record, when, and under what policy.
Source code is a different animal entirely. It isn’t regulated in the way customer data is, but it is the asset an acquirer, a competitor, or a departing engineer would value most. Source code loss usually isn’t a breach in the legal sense, it’s a competitive one, and it rarely trips the same alerts because it doesn’t look like “sensitive data” to a regex-based classifier. A file full of proprietary algorithms just looks like text.
This is where context-aware classification earns its keep over pattern matching. A platform that only recognizes sensitive data by format (a credit card number, a Social Security number) has no way to flag a .py file containing a pricing engine, or a Slack message with an internal API key pasted into it. Data classification software needs document and code context, not just regex, to catch both asset classes with one policy engine.
Where Does Source Code Actually Leave the Company?
Generic DLP built for customer-data protection focuses on file uploads and email attachments. Source code leaves through paths that are native to how developers work, and most of them are invisible to tools that only watch SaaS apps or network traffic:
- Local repository clones. A developer clones a private repo to a laptop, then that laptop syncs to a personal cloud drive, gets backed up to an external SSD, or leaves the building entirely. The exposure happens at the endpoint, not the git server.
- AI coding assistants. Pasting a function into a chat-based coding assistant to debug it, or letting an autonomous coding agent read a repository to refactor it, moves proprietary logic outside company infrastructure. This is a known category of GenAI risk: accidental data leakage happens when employees paste or upload proprietary data into AI tools, and the same mechanism applies to code as much as to spreadsheets.
- Personal package registries. Publishing an internal package to a personal npm or PyPI account, even temporarily for testing, can expose internal logic publicly if the package isn't unpublished cleanly.
- Pasted snippets in support tickets. An engineer troubleshooting a customer issue pastes a code block containing internal comments, credentials, or architecture details into a third-party support tool or ticketing system that isn't on the security team's radar.
None of these paths involve a malicious actor. They’re workflow, not insider threat. A developer using an AI assistant to move faster isn’t circumventing security, they don’t know where the boundary is, because most DLP tools have never drawn one at the endpoint. This is exactly why endpoint DLP solutions need visibility into clipboard activity, browser uploads, and GenAI paste and upload activity, not just file-level scanning.
How Does a Customer Security Questionnaire Turn DLP Into a Revenue Problem?
A separate but related problem is that DLP gaps stop being a security issue the moment a customer’s procurement team asks about them. Mid-market SaaS companies selling into fintech, healthcare, or insurance buyers routinely face security questionnaires and vendor risk assessments before a contract closes. These questionnaires ask specific, auditable questions: Do you have DLP on endpoints? Can you show data lineage for customer records? How do you prevent employees from pasting customer data into unapproved AI tools like ChatGPT?
If the honest answer is “we have some SaaS app monitoring but no endpoint coverage,” that’s a stalled deal, not just a gap on a roadmap. SOC 2 and ISO 27001 both require an independent audit of security controls and, for ISO 27001, a documented Information Security Management System; the tooling in place can support these controls, but certification still depends on how the organization configures, operates, and documents its program. Neither carries a direct regulatory fine for gaps, but the practical cost is losing the certification itself, and with it, the enterprise contracts that require it as a precondition. For a mid-market SaaS company, DLP maturity is increasingly a sales enablement function as much as a security one.
This is also where covering more compliance controls from a single agent matters operationally. A platform built with core DLP and real-time enforcement can help address a wider set of SOC 2 and ISO 27001 controls from the same deployment, which shortens the list of point tools a lean IT team has to stand up and maintain before the next audit cycle.
What Should a Mid-Market SaaS Company Look For in a DLP Platform?
Once the two asset classes and the revenue pressure are clear, the real question is what to actually evaluate for. Five things matter more than a long feature list:
- Real Linux support. Most engineering teams run a meaningful share of developer workstations on Linux. A DLP platform that only covers Windows and macOS has a structural blind spot on exactly the machines closest to source code.
- Context-aware classification, not just regex, so code, contracts, and customer PII are all recognized by what they are, not just how they're formatted.
- GenAI and coding-assistant visibility, including shadow AI discovery, since AI coding tools are now a default part of developer workflow rather than an edge case.
- Real-time enforcement at the point of risk, meaning the platform can allow, warn, coach, block, or isolate at the moment of the action, rather than only logging it after the fact.
- One agent, not five, because a mid-market security team rarely has headcount to run separate tools for endpoint DLP, SaaS monitoring, and GenAI security.
Kitecyber’s See, Decide, Enforce model is built around this approach: one lightweight agent discovers and classifies data by context across files, clipboard, browser, email, SaaS apps, data pasted or uploaded into GenAI tools, and removable media, decides using full data lineage, and enforces in real time, on Windows, macOS, and native Linux.
How Do the Leading DLP Platforms Compare for This Use Case?
|
Platform |
Deployment model |
Linux endpoint support |
Best fit note
|
|
Kitecyber |
Endpoint-native agent, cloud-managed |
Native Windows, macOS, and Linux |
Best for mid-market SaaS teams wanting one agent for customer data, source code, and GenAI/coding-assistant risk together |
|
Cyberhaven |
Cloud console with endpoint agents and browser extensions |
Requires agent/extension deployment for full lineage |
Strong data lineage tracing; worth evaluating if lineage visibility is the top priority |
|
Nightfall |
Cloud-native, API-first, with an endpoint agent |
Depends on agent coverage; core detection is cloud-based |
Good for SaaS and GenAI app coverage where API connectivity is acceptable |
|
Endpoint Protector |
Appliance, virtual appliance, or cloud, with endpoint agents |
Windows, macOS, and Linux |
Established device-control and content-aware DLP; endpoint-focused rather than broad network inspection |
|
Safetica |
On-premises or cloud-native, endpoint agents |
Endpoint-agent based; check current Linux coverage |
Solid mid-market insider risk and DLP option; teams with heavy scanned-document workflows should validate OCR accuracy on low-quality images as part of evaluation |
|
Microsoft Purview |
Cloud-native, integrated into Microsoft 365/Azure |
Built for M365-centric environments |
Natural fit if the company is fully Microsoft-centric, less native for mixed-OS engineering teams |
Kitecyber is built as an endpoint-native agent that pairs DLP with source code and GenAI/coding-assistant visibility on Windows, macOS, and native Linux; it fits mid-market SaaS teams that want one deployment covering both customer data and developer workflow risk, though, like any single-agent approach, it asks a security team to commit to one platform rather than spreading coverage across specialized point tools.
Cyberhaven is genuinely strong at data lineage tracing, following a piece of data as it moves and transforms across systems, which makes it a good fit for teams whose top priority is understanding exactly where sensitive data has traveled. The tradeoff is that full lineage visibility depends on agent and browser extension deployment across the fleet, which adds rollout overhead compared to a single unified agent.
Nightfall is API-first and cloud-native, which makes it a natural fit for teams whose primary exposure is SaaS and GenAI app content rather than endpoint activity. Its endpoint coverage depends on agent deployment, so teams whose main risk is local file and clipboard activity on developer machines may find the endpoint story thinner than the SaaS app story.
Endpoint Protector has a long track record in device control and content-aware DLP, with genuine Windows, macOS, and Linux agent support. It is a solid choice for teams whose priority is granular device and port control, though its strength is more endpoint policy enforcement than broad network-level inspection.
Safetica offers solid mid-market insider risk and DLP capability with an endpoint-agent model. Teams evaluating it should confirm current Linux coverage against their fleet and, if document scanning is part of the workflow, validate OCR accuracy on lower-quality images during a proof of concept.
Microsoft Purview is a natural fit for organizations already standardized on Microsoft 365 and Azure, since it is deeply integrated into that ecosystem. It is less native for mixed-OS engineering teams running significant Linux infrastructure, where coverage and policy parity with Windows/macOS should be tested directly.
Honest caveat: no platform in this table, including Kitecyber, can claim to prevent every possible path a determined person could use to move source code out of a company. The realistic bar is closing the ordinary, high-volume paths, clones, pastes, uploads, and GenAI activity, so that what’s left is the rare, deliberate case rather than routine workflow leakage.
Is Kitecyber a Zscaler Alternative for This Use Case?
Teams evaluating Zscaler for this problem are usually solving a different question than DLP. Zscaler’s Zero Trust Exchange is a cloud-native platform for secure any-to-any connectivity and zero trust access, delivered through lightweight endpoint agents or tunnels. It is strong at controlling network-level access to applications. It is not built as an endpoint-native DLP engine watching clipboard, file movement, and GenAI paste and upload activity at the point of risk.
For a mid-market SaaS company whose real exposure is a developer’s laptop, not network access policy, Kitecyber provides data exfiltration prevention: the same lightweight agent that classifies and enforces DLP policy also handles private access control, so teams consolidating away from an SSE-first stack get data protection and access control from one deployment instead of layering a DLP tool on top of a network security platform.
About Kitecyber
Kitecyber is a data loss prevention company built for the GenAI era, protecting sensitive data at the endpoint, where customer records and source code actually move. One lightweight agent covers Windows, macOS, and native Linux, discovering and classifying sensitive data by context, tracking full data lineage, and enforcing policy in real time across files, clipboard, browser, email, SaaS apps, GenAI paste and upload activity, and removable media. Kitecyber’s See, Decide, Enforce model applies that same DLP engine to insider risk and GenAI security, helping mid-market SaaS, fintech, healthcare, and regulated-industry teams innovate with confidence.
See verified customer reviews of Kitecyber on G2 and SourceForge.
Frequently Asked Questions
Endpoint DLP can detect when proprietary code is pasted into a GenAI tool and enforce a policy in real time, warn, coach, block, or log, but it works by governing the action, not by disabling the tool. The goal is visibility and control, not banning AI assistants outright.
Not inherently, but many DLP platforms have historically had weaker or no Linux agent support, which means engineering teams running Linux workstations are often the least monitored, regardless of actual risk level.
API-based tools are effective for SaaS app content, but source code exposure frequently happens at the endpoint, in a local clone, a clipboard paste, or an AI assistant paste or upload, before it ever reaches a SaaS app the API can see.
Vendor risk assessments and SOC 2-aligned questionnaires commonly ask about data loss prevention controls, insider risk monitoring, and GenAI usage policy, making DLP maturity a documented part of the sales cycle for regulated-industry buyers.
The classification logic differs: IP protection needs to recognize source code, design files, and internal documents by content and context, while customer-data DLP is often built primarily around recognizing regulated data formats like payment or health information. A platform that only does one will under-protect the other.
DLP pricing varies by vendor and typically scales with number of endpoints or users covered and the range of channels monitored (endpoint, SaaS, email, GenAI); specific pricing should be confirmed directly with each vendor.
With over a decade of experience steering cybersecurity initiatives, my core competencies lie in network architecture and security, essential in today's digital landscape. At Kitecyber, our mission resonates with my quest to tackle first-order cybersecurity challenges. My commitment to innovation and excellence, coupled with a strategic mindset, empowers our team to safeguard our industry's future against emerging threats.
Since co-founding Kitecyber, my focus has been on assembling a team of adept security researchers to address critical vulnerabilities and enhance our network and user security measures. Utilizing my expertise in the Internet Protocol Suite (TCP/IP) and Cybersecurity, we've championed the development of robust solutions to strengthen cyber defenses and operations.
Posts: 99
With over a decade of experience steering cybersecurity initiatives, my core competencies lie in network architecture and security, essential in today's digital landscape. At Kitecyber, our mission resonates with my quest to tackle first-order cybersecurity challenges. My commitment to innovation and excellence, coupled with a strategic mindset, empowers our team to safeguard our industry's future against emerging threats.
Since co-founding Kitecyber, my focus has been on assembling a team of adept security researchers to address critical vulnerabilities and enhance our network and user security measures. Utilizing my expertise in the Internet Protocol Suite (TCP/IP) and Cybersecurity, we've championed the development of robust solutions to strengthen cyber defenses and operations.
Posts: 99