A contractor pastes proprietary source code into a public AI chatbot. A remote employee uploads a customer list to a personal cloud drive from a coffee shop network. Neither action touches your firewall. Neither one trips a gateway alert. It happens on the endpoint, where Netskope vs Fortinet and most SASE platforms simply do not look.
That blind spot is exactly why so many security teams end up comparing these two vendors in the first place. Fortinet and Netskope both sit near the top of the Security Service Edge market on Gartner Peer Insights, and both get pulled into shortlists for very different reasons. This guide breaks down where each one wins, where each one falls short, and why Kitecyber has become the platform teams check before signing either contract.
TL;DR
- Netskope leads on cloud-native CASB, DLP, and SaaS visibility, but ships with no native SD-WAN.
- Fortinet leads for branch-heavy enterprises already standardized on FortiOS and Fortinet hardware.
- Both platforms route traffic through cloud gateways or appliances, adding latency and missing endpoint-level activity.
- Neither platform natively governs what AI agents do once they run on a device with a user’s credentials.
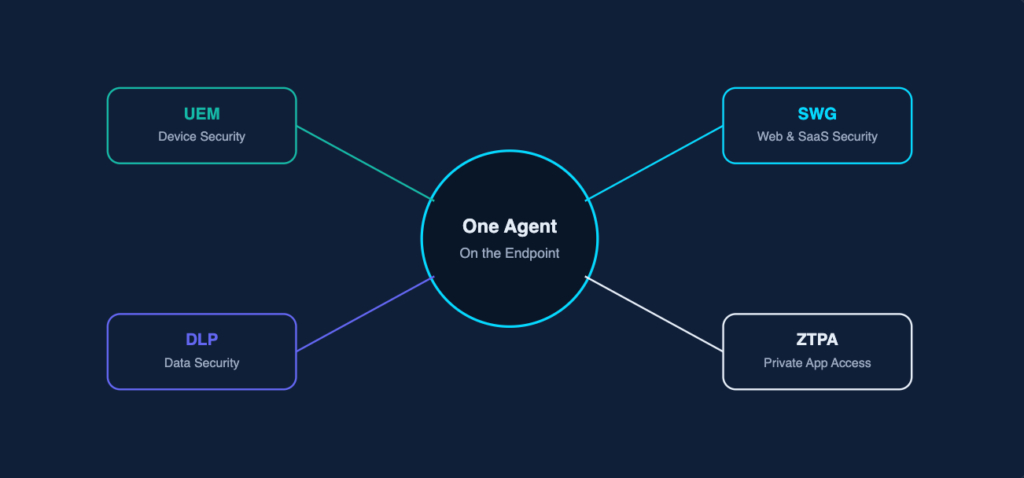
- Kitecyber runs device security, web security, data security, and private app access from one endpoint agent, with no gateway in the traffic path.
What Do Netskope and Fortinet Actually Do in a SASE Stack?
SASE, short for secure access service edge, combines networking and security functions like secure web gateway (SWG), cloud access security broker (CASB), firewall as a service, and zero trust network access into one cloud-delivered model. The goal is simple. Users, apps, and devices get consistent protection no matter where they connect from.
Netskope built its name as a cloud access security broker before expanding into a full SASE platform. Its architecture is cloud-native from the ground up, which makes it a strong fit for organizations with heavy SaaS adoption. Fortinet took a different route. It built its SASE offering, FortiSASE, on top of decades of firewall and SD-WAN experience, delivered through a single operating system called FortiOS.
Where Does Netskope Pull Ahead?
1. Deep SaaS and Cloud Visibility
Netskope maps traffic to specific cloud apps and activities rather than just ports and IPs, which gives security teams granular control over sanctioned and unsanctioned SaaS use.
2. Strong DLP Heritage
Netskope pioneered the CASB category and carries that data-centric approach into its DLP policies across web and cloud traffic.
3. Cloud-Native Scaling
Its NewEdge infrastructure scales automatically with demand, which removes the hardware constraints that come with appliance-based platforms.
One reviewer on Gartner Peer Insights described their Netskope One SSE deployment as delivering strong visibility, granular policy control, and reliable data protection across SaaS, web, and private applications.
The tradeoff shows up the moment your network gets complicated. Netskope does not ship native SD-WAN, a gap that independent research on Netskope alternatives points to directly as a real limitation for enterprises with many branch locations.
Best for: cloud-first organizations that need deep SaaS visibility and DLP more than branch network consolidation.
Where Does Fortinet Pull Ahead?
1. Native SD-WAN Integration
FortiSASE runs on the same FortiOS that powers Fortinet’s SD-WAN and branch firewalls, which closes the gap Netskope leaves open for distributed offices.
2. Unified Management Across 50+ Products
FortiOS gives teams one policy engine across dozens of Fortinet product lines, which cuts down on the number of consoles admins need to manage.
3. High-Throughput Hardware Acceleration
Custom ASIC processors in FortiGate appliances help maintain performance under heavy network load, a detail enterprise buyers with high traffic volumes value.
On Gartner Peer Insights, Fortinet holds a higher overall star rating than Netskope, with reviewers highlighting the shift away from legacy, perimeter-based VPNs toward zero trust as a genuine improvement. Support quality comes up as a recurring concern in the same reviews, with more than one reviewer noting that FortiSASE performs well but support response times need work.
Best for: enterprises already standardized on Fortinet hardware, especially those with a large branch footprint.
Why Do Teams Look for a Netskope or Fortinet Alternative?
Both platforms share the same architectural limitation. They inspect traffic as it passes through a cloud gateway or appliance. That works well for web and cloud traffic. It does not extend down to what happens locally on the device itself.
Terminal commands, local file access, copy-paste actions, and increasingly, AI agent activity, all happen at the endpoint, not on the wire. An IBM 2025 data breach analysis found that shadow AI, meaning unsanctioned AI tools used without IT oversight, added significant cost to breaches that involved it, and most of that activity never crosses a network gateway at all.
This is the exact reason Kitecyber’s approach to data exfiltration starts at the endpoint instead of the network edge.
How Does Kitecyber Compare to Both Platforms?
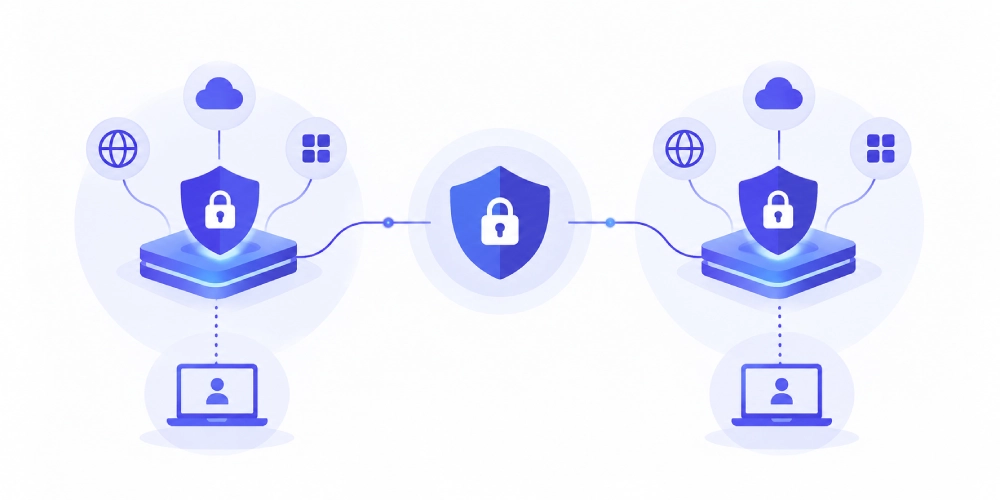
Kitecyber runs a different playbook entirely. Instead of backhauling traffic to a cloud gateway, it enforces device security, web security, data security, and private app access directly from a single lightweight agent installed on the endpoint itself.
Kitecyber’s single-agent architecture: device management, web security, data loss prevention, and zero-trust private access all run through one endpoint agent, with no cloud gateway in the traffic path.
1. No Cloud Gateway, No Hairpinning
Traffic gets inspected locally on the device, so there is no added latency and no single point of failure if a gateway goes down.
2. Endpoint-Level Visibility
Kitecyber sees terminal commands, file access, and copy-paste activity, the same layer where AI agents now operate with a user’s full privileges.
3. Native SD-WAN Coverage Not Required
Since there is no backhaul to a gateway, branch office topology matters far less than it does for Netskope or Fortinet.
4. GenAI and Shadow SaaS Governance
Kitecyber blocks sensitive data from leaving through unsanctioned AI tools like ChatGPT, Gemini, and Perplexity, an area neither Netskope nor Fortinet was purpose built to cover.
5. Zero-Touch Deployment
One agent replaces four separate point tools, which cuts rollout time from weeks of integration work down to minutes.
6. Shared Device-Trust Engine
All four modules share the same trust context, so policies stay in sync instead of drifting apart across separate consoles.
The Bottom Line: Who wins in Netskope vs Fortinet SASE Debate?
None. As the use-case differs. Pick Fortinet if your branch offices already run on FortiGate hardware and you want SASE under the same operating system. Pick Netskope if cloud app visibility and DLP for a SaaS-heavy workforce matter more to you than SD-WAN consolidation.
If you want a platform that also protects what happens at the endpoint itself, including AI agent activity, GenAI usage, and local file movement, Kitecyber gives you that coverage from one agent instead of stitching together point tools.
See Why Security Teams Are Switching to Kitecyber
Book a live walkthrough and see how Kitecyber unifies device, web, data, and private app security into one endpoint agent, with zero-touch deployment and no cloud gateway required.
Frequently Asked Questions