Approved Isn't Static: Catching When a Sanctioned AI Tool Changes Behavior

Quick Answer: AI Security Posture Management (AISPM), also called AI Posture Management, is the continuous process of discovering, monitoring, and controlling how AI tools, models, and agents interact with your company's data and systems. It covers everything from spotting an unapproved AI app on someone's laptop to blocking a customer record from being pasted into a public chatbot. Most teams that manage AI posture well pair a discovery layer with policy enforcement at the point where employees actually use AI, which is the endpoint.

Kitecyber | Data & Gen AI Security

Your AI approval process answers one question once. Attackers and updates ask it every day.

On 29 October, Netskope published a post on finding the AI risks that matter in a flood of AI activity. One point deserves attention beyond its own product: risk emerges through patterns, and the risk profile of an approved connection is not fixed. Netskope cites Microsoft’s June 2026 demonstration of how a change to an already-approved MCP tool could cause an agent to send invoice data to an external server.

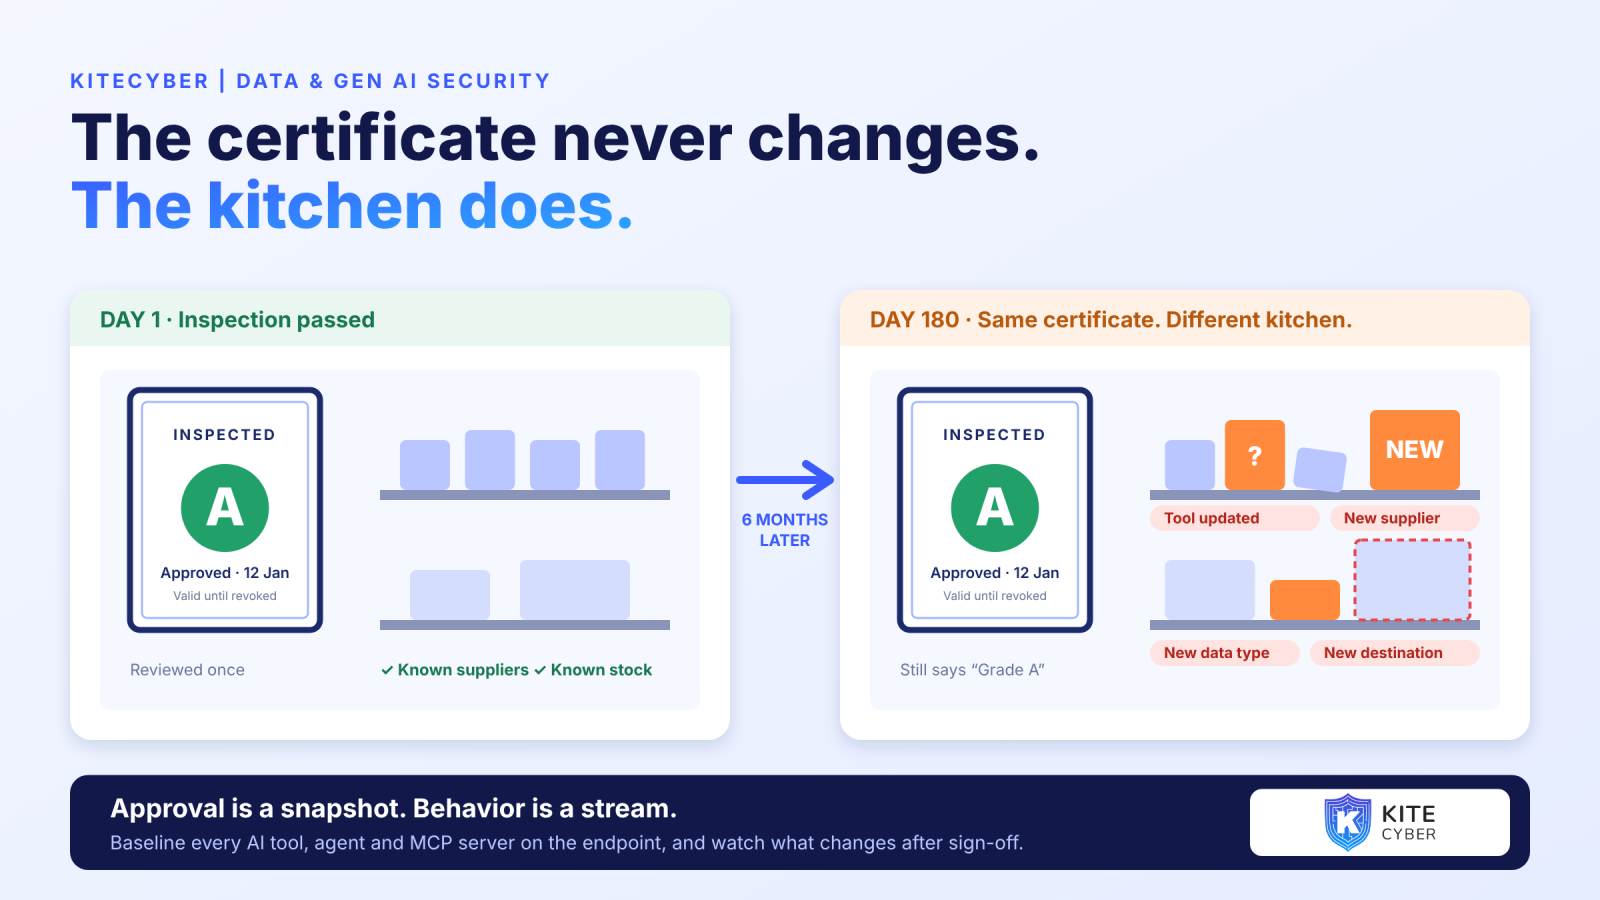
That is the gap in most AI governance programs. Approval is a snapshot. Behavior is a stream.

Why a point-in-time approval decays

Consider what can change after a tool passes review:

Netskope’s observation applies: each of these can look reasonable in isolation. Only the combination shows the drift.

The correlation problem

The same post cites a Cybersecurity Insiders and Netskope survey in which 51% of security teams say scattered context and signals slow investigations, and only 9% can effectively correlate users, devices, applications and network paths. (Figures are the cited source’s own.) Drift detection fails for the same reason: the evidence lives in different systems.

What the endpoint contributes

A baseline needs a consistent subject. On the device, the subject is concrete: this process, run by this user, on this device with this posture, talking to these destinations and touching these data classes. From that you can track, per tool or agent:

None of these require reading prompt content. Counts, categories, destinations and timing are enough to rank what deserves a human look.

From drift to action

Not every change is a problem, and Netskope is right that more AI activity is not automatically more risk. A practical model: low-risk drift generates a note in the audit trail, medium-risk drift prompts a review of the tool’s tier, and drift involving sensitive data classes or a new external destination can trigger a warning or block under existing policy.

Where Kitecyber fits

Kitecyber’s Gen AI and data security runs on the endpoint, so process, user activity, network activity, device posture and data classification (80+ categories) are available in one place. That is the context a baseline needs. A lightweight agent (under 2% CPU) and typical deployment in around a day make it practical to start measuring drift without a long project.

Book a Kitecyber walkthrough at kitecyber.com to see how endpoint context supports ongoing, not one-time, AI governance.

Ajay Gulati

Ajay Gulati is a passionate entrepreneur focused on bringing innovative products to market that solve real-world problems with high impact. He is highly skilled in building and leading effective software development teams, driving success through strong leadership and technical expertise. With deep knowledge across multiple domains, including virtualization, networking, storage, cloud environments, and on-premises systems, he excels in product development and troubleshooting. His experience spans global development environments, working across multiple geographies. As the co-founder of Kitecyber, he is dedicated to advancing AI-driven security solutions.

Scroll to Top