Table Of Content
Small Bugs, Long Chains: What Agent Kill-Chain Research Says About Endpoint Controls
-
November 5, 2026
-
Each flaw looks like a local bug. Chained together on a shared machine, they end at a privileged cloud identity.
On 3 November Cymulate published a write-up of its SecTor 2026 talk, “Across the Kill Chain: How Agents Became the Enterprise’s New Front Door.” The team examined agents that ship with deep host access, including Claude Code, Codex CLI, Cursor CLI, Gemini CLI, GitHub Copilot CLI, AWS Kiro and Google Antigravity, and grouped earlier findings into recurring patterns: execution flow hijacking, sandbox escape, world-writable trust, cross-user inter-process communication takeover and UNC credential coercion.
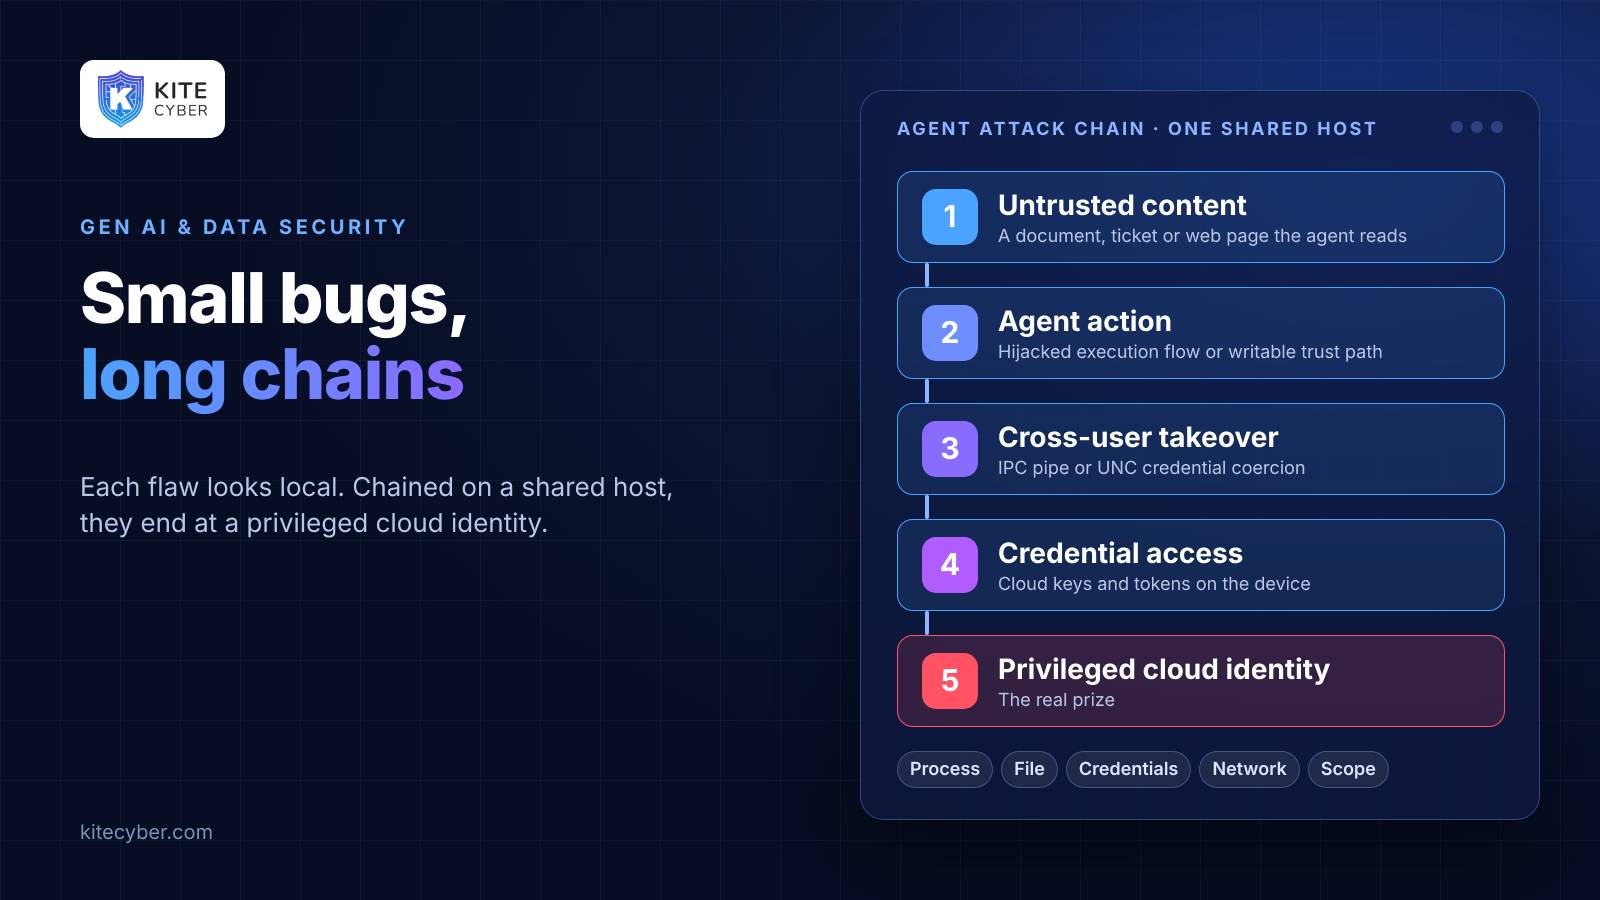
The new point is the chaining. In two enterprise scenarios, both starting from content an agent reads, the attacker crosses from one Windows user to another on a shared host and ends with a privileged cloud identity. As the authors put it, the valuable thing is rarely the endpoint itself: it is the cloud identity, shared data and automation pipelines the endpoint can reach.
The same day, the Microsoft Digital Defense Report 2026 summary added scale. It reports that four techniques accounted for roughly 90% of observed attack activity in Azure AI workload telemetry: malicious link injection (52%), jailbreaks (16%), tool and agent abuse (12%), and identity and credential abuse (10%). It also flags memory poisoning, where content placed where an agent reads can end up where it remembers.
What this means for a fleet of laptops
- The unit of risk is the chain, not the bug. Patching one agent flaw matters, but a defender who only tracks individual CVEs misses the path. The path is: untrusted content, then agent action, then local privilege or credential access, then a cloud identity.
- The sandbox is not the boundary. Cymulate's guidance says it directly: a vendor sandbox should not be your only security boundary, and real isolation, such as a VM or dedicated container host, is preferable for agent actions touching credentials and sensitive data.
- Exact-action baselines are brittle. The research recommends baselining the scope of work instead: which tasks, data and destinations each agent is supposed to touch. That is a policy about context, and context lives on the device.
Checks the endpoint can make
- 1.Inventory agents and their versions per device, including CLIs and IDE-embedded tools, and flag shared or multi-user hosts where several people run agents
- 2.Watch for the building blocks of a chain: new executables in agent search paths, writable trust directories, unexpected inter-process pipes, and outbound connections to UNC or SMB destinations from agent processes.
- 3.Classify what agents read and where credentials sit, so a read of a cloud credential file by an agent process is an event with meaning rather than noise.
- 4.Define scope per agent (data classes, destinations, devices) and alert on exits from that scope instead of on every action.
- 5.Gate on posture and ownership. Sensitive repositories and cloud-credential workflows belong on managed, healthy, single-user devices.
None of this removes the need for patching or for the vendors to fix the underlying flaws. It narrows the blast radius while they do.
Where Kitecyber fits
Kitecyber’s endpoint agent (under 2% CPU) brings together device posture, process and operating system activity, user activity, network activity and data classification across 80+ categories. For chained agent attacks, that means seeing the links as one story on a device: which agent process read which classified file or credential, what it spawned, and where it connected, with policy enforced on the same device and an audit trail. Typical deployment takes around a day with pre-built compliance policies.
Book a Kitecyber walkthrough at kitecyber.com to see agent activity chains on your own endpoints.

Ajay Gulati
Ajay Gulati is a passionate entrepreneur focused on bringing innovative products to market that solve real-world problems with high impact. He is highly skilled in building and leading effective software development teams, driving success through strong leadership and technical expertise. With deep knowledge across multiple domains, including virtualization, networking, storage, cloud environments, and on-premises systems, he excels in product development and troubleshooting. His experience spans global development environments, working across multiple geographies. As the co-founder of Kitecyber, he is dedicated to advancing AI-driven security solutions.