Table Of Content
Detection Alone Falls Short:What Regulators Now Expect for AI, and Why It Lands on the Endpoint
-
November 7, 2026
-
Kitecyber | Data & Gen AI Security
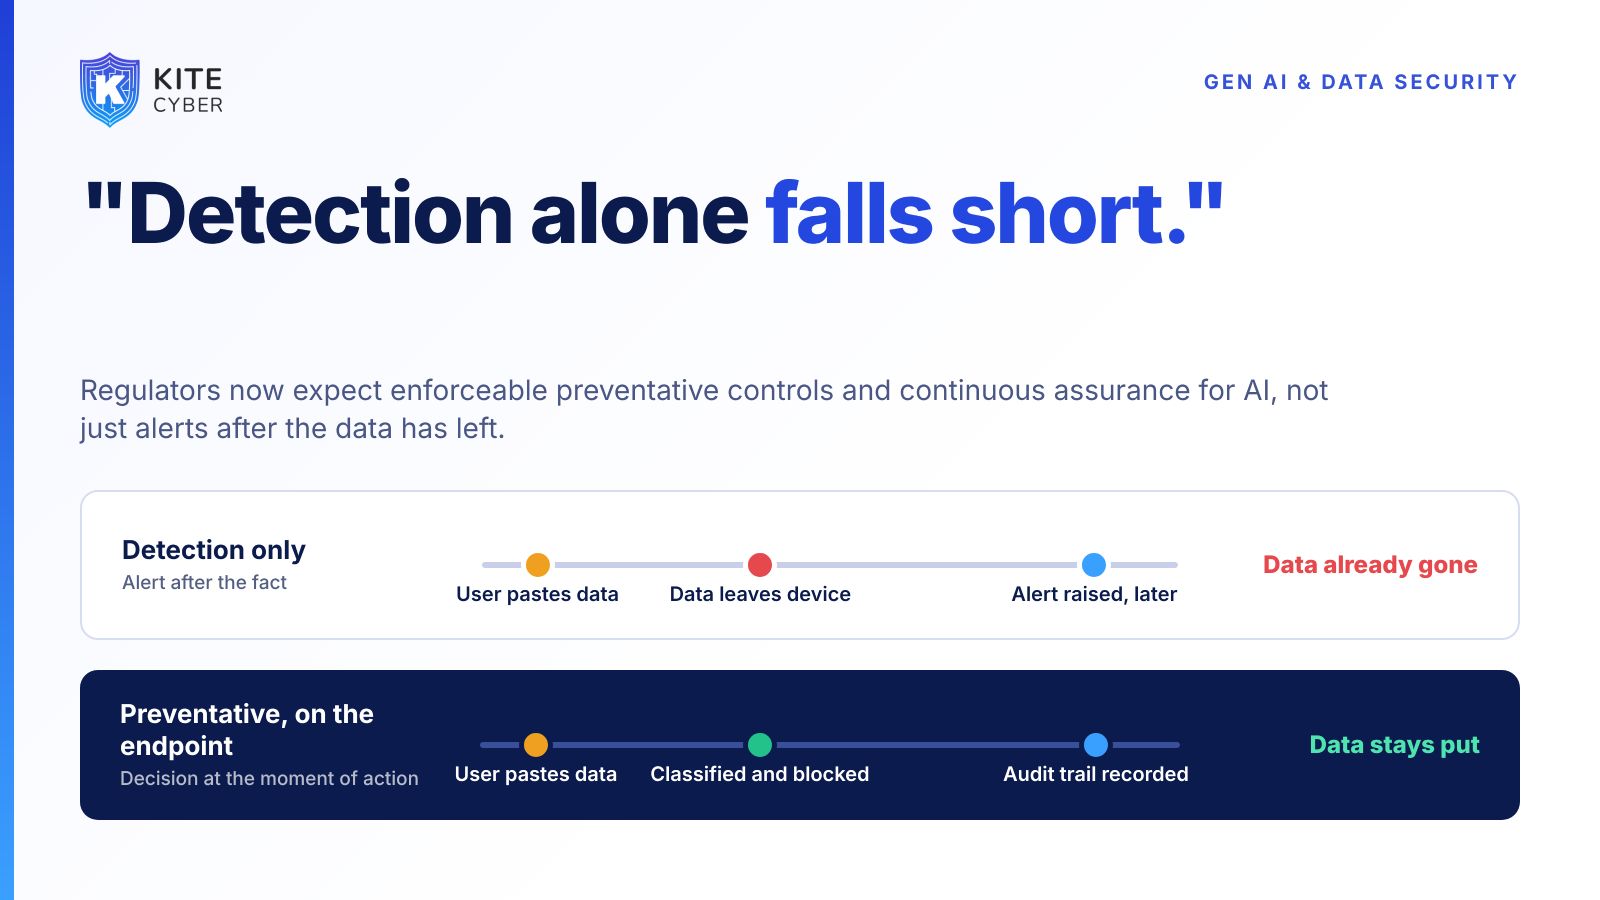
A Zscaler blog on Australia’s APRA standards quotes the regulator’s April 2026 AI letter: it expects enforceable preventative controls and continuous assurance, and says policy direction and after-the-fact detection on their own fall short. For AI use, that expectation has to be met where the data and the tools actually are.
On 6 November, Zscaler published a blog on APRA’s CPS 230 and CPS 234 standards. Its closing section extends the argument to AI. Per Zscaler, APRA’s April 2026 letter on artificial intelligence notes that AI agents, AI built into supplier platforms and staff using unapproved AI tools bring new identities, new data flows and new fourth-party dependencies, and that APRA expects enforceable preventative controls and continuous assurance, with policy direction and after-the-fact detection alone falling short. Zscaler also reports that both standards are now fully in effect, so the question for financial institutions has moved from design to whether the evidence holds up.
APRA regulates Australian financial institutions, but the shift in wording is broader than one jurisdiction. Written policy and alerts that fire after a leak are no longer being treated as sufficient for AI.
What "preventative" and "continuous" demand in practice
Read plainly, the expectation has three parts, each of which is hard to meet from a distance:
- Prevent at the moment of action. A rule that blocks a paste of customer data into an unapproved AI tool, or a push of source code to a personal repository, has to run before the data leaves, not in a report the next morning.
- Cover the tools nobody approved. Staff using unapproved AI tools is named as a risk. Prevention needs discovery of those tools, including desktop apps, browser extensions, local agents and MCP servers, not just the sanctioned list.
- Produce evidence continuously. Assurance means being able to show, for any user, device or agent, what was allowed, warned or blocked, and why. Screenshots at audit time do not do this.
Why the endpoint is the natural enforcement point
The device is where a person types a prompt, an agent reads files, and data is copied between applications. It is also where context is richest:
- Device posture: is this a managed, healthy device, or not?
- Process and operating system activity: which application or agent touched the data, not just which website was visited.
- Data classification: what the content actually is, across categories such as source code, customer records and credentials, rather than guessing from a destination.
- User and network activity: who the user is, which account (work or personal) they used, and where the data went.
Network-level controls remain valuable and complement this. But traffic that is encrypted, local, or never routed through the gateway, such as a local agent writing to a file or an app on a personal account, is easier to judge with on-device context.
A practical checklist
- 1.Write the policy as enforceable rules, not guidance: which data classes may go to which AI tools, for which users and device states.
- 2.Discover before you enforce. Inventory AI tools, extensions, agents and servers actually in use, including unapproved ones.
- 3.Start with warn, move to block for the highest-risk data classes, and tune with real events.
- 4.Keep an audit trail per decision: user, device, process, data class, action, outcome.
- 5.Review continuously, for example monthly, against what changed: new tools, new accounts, new agents.
- 6.Map the controls to your framework (for example APRA CPS 234, the EU AI Act, NIST AI RMF) so evidence answers the regulator's question directly.
Where Kitecyber fits
Kitecyber’s Gen AI and data security runs on the endpoint, combining device posture, operating system and process activity, user activity, network activity and data classification across 80+ categories. It discovers Gen AI tool use, applies allow, warn or block policy at the moment of action, and records an audit trail that can serve as ongoing evidence. The lightweight agent (under 2% CPU) typically deploys in about a day. It is not a substitute for governance, and the right control set depends on your regulatory obligations.
Book a Kitecyber walkthrough at kitecyber.com to see preventative AI controls and audit evidence in one view.

Ajay Gulati
Ajay Gulati is a passionate entrepreneur focused on bringing innovative products to market that solve real-world problems with high impact. He is highly skilled in building and leading effective software development teams, driving success through strong leadership and technical expertise. With deep knowledge across multiple domains, including virtualization, networking, storage, cloud environments, and on-premises systems, he excels in product development and troubleshooting. His experience spans global development environments, working across multiple geographies. As the co-founder of Kitecyber, he is dedicated to advancing AI-driven security solutions.