A company with 250 to 1,000 employees needs data loss prevention software that a lean team, usually one to five people, can deploy and tune without a dedicated DLP analyst or a professional services engagement. The right shortlist for this size band includes Kitecyber, Safetica, Nightfall, Cyberhaven, Endpoint Protector, Netwrix, and Forcepoint, each strong in a different scenario. The mid-market buyer’s real constraint isn’t feature count. It’s operational overhead: whichever tool gets picked has to run with existing headcount and protect sensitive data as it moves through endpoints, cloud apps, browser uploads, and data pasted or uploaded into GenAI tools.
TL;DR
About the Author: This article is published by
Kitecyber, a
data loss prevention (DLP) company built for companies from 250 to 1,000 employees whose endpoint-native platform is used by growth-stage fintech, healthcare, and GenAI companies to run DLP with security teams of two to four people.
What Should a 250 to 1,000 Employee Security Team Look for in DLP Software?
A company at this size is past the point where spreadsheet-based access reviews and ad hoc USB restrictions are defensible to an auditor, but it hasn’t reached the point where it can staff a full DLP program with dedicated analysts. That gap defines the entire buying decision. Data loss prevention software at this stage needs to answer three questions on its own, largely without a human tuning policy every week: where is sensitive data, who is moving it, and should that movement be allowed.
Compliance pressure adds urgency. Frameworks like SOC 2, ISO 27001, HIPAA, and PCI DSS call for documented policies for data minimization, third-party data handling, and breach response, and GDPR and CCPA add specific data access and deletion rights that have to be operationally provable, not just written down. Getting these controls wrong carries real cost: under GDPR, fines can reach up to 4% of a company’s global annual revenue for the preceding financial year, per Article 83 of the regulation. A mid-market team evaluating data classification software or sensitive data discovery tools needs to weigh each option against how much ongoing tuning it demands, not just its feature list.
Why Is the Enterprise DLP Shortlist the Wrong Answer at This Size?
The enterprise DLP shortlist assumes a security operations function with headcount and infrastructure that most 250 to 1,000 employee companies don’t have. Symantec DLP, for example, delivers granular control for large organizations but its architecture requires a central Enforce Server plus separate endpoint agents and dedicated network appliances for web and email monitoring, and it’s built around the assumption of a dedicated SOC managing that stack. Digital Guardian and Trellix follow a similar pattern: hybrid architectures combining endpoint agents with dedicated hardware or virtual appliances for network-level inspection, which means someone on staff has to manage appliance clusters in addition to policy.
That’s not a knock on those products’ capability at enterprise scale. It’s a mismatch of operating model. A five-person security team doesn’t have a spare engineer to rack and patch a DLP appliance, and it doesn’t have an analyst whose full-time job is triaging false positives from static regex rules. The practical requirement at this headcount is a deployment that a generalist IT or security hire can stand up in days, not a rollout that needs a services engagement to reach production.
What Changes When Data Leaves Through Browser Uploads and GenAI Tools?
Building on the deployment problem above, the harder issue is that the exfiltration path itself has shifted. Traditional DLP was built to watch network egress: email gateways, web proxies, USB ports. Today, an employee pasting a customer list into ChatGPT, or a copilot summarizing a confidential file and posting it to a connected app, never touches a network appliance at all. Modern DLP has to classify the data users paste and upload into AI tools at the moment it enters them, catch shadow AI usage across browser and API interactions with tools like ChatGPT and Claude, and enforce policy at the point where the user or the agent is acting, not at a chokepoint the data may never pass through.
This is why endpoint-native architecture matters more at this size than it did five years ago. A tool that only sees traffic it can route through its own infrastructure misses activity that happens locally in a browser tab or a clipboard paste before anything is transmitted. Sensitive data discovery tools and data lineage tracking tools now need visibility into that local layer to be complete, and this is the exact gap that frameworks like the OWASP GenAI LLM Top 10 and MITRE ATLAS have been developed to address.
Which DLP Platforms Should Be on the Mid-Market Shortlist?
Here is a working shortlist of seven platforms for a 250 to 1,000 employee team, each named for what it does well and what to watch for.
Kitecyber: Endpoint-Native DLP With GenAI Security Built In
Kitecyber is a data loss prevention company that delivers endpoint-native DLP through one lightweight agent covering Windows, macOS, and native Linux endpoints, browser, clipboard, email, SaaS/cloud apps, and removable media. It runs a continuous See, Decide, Enforce loop: it discovers sensitive data with context-aware classification, tracks data lineage as files and content move, and enforces the right action (allow, block, warn, coach, log, or isolate) at the point of risk in real time. Because the same agent helps address more SOC 2, ISO 27001, HIPAA, and PCI DSS controls than a pure DLP point product without adding a second deployment, it delivers compliance breadth alongside data protection. Best fit: mid-market teams that want DLP and shadow GenAI visibility from a single agent. Limitation: as a newer entrant, it has a smaller reference base than long-established enterprise suites, so buyers should validate against their specific SaaS app list during a trial.
Safetica: Endpoint and Cloud DLP Purpose-Built for Mid-Market
Safetica offers both on-premises and cloud-native deployments via endpoint agents, with no dedicated network appliance required. It covers
data discovery, workspace monitoring, and
device control. Best fit: teams wanting a straightforward DLP and insider risk tool without appliance overhead. Limitation: its OCR can struggle with low-quality scanned images, which matters for document-heavy compliance workflows.
Nightfall: Cloud-Native DLP for SaaS and GenAI Apps
Nightfall integrates with cloud applications via APIs and also offers an endpoint agent, operating entirely in the cloud without on-premises appliances. It uses AI-powered detection and automated remediation across SaaS and endpoints. Best fit: teams whose primary exposure is SaaS and GenAI app sprawl rather than device-level data movement. Limitation: its core detection engine depends on cloud connectivity.
Cyberhaven: Data Detection and Response Focused on Lineage
Cyberhaven traces
data lineage and movement across endpoints and cloud using a cloud-based console paired with endpoint agents and browser extensions, with no network appliance needed. Best fit: teams whose top priority is tracing exactly how a specific file moved and mutated before exfiltration. Limitation: full lineage capture depends on the agent or extension actually being deployed on every device in scope.
Endpoint Protector: Cross-Platform Device Control
Endpoint Protector (by Netwrix) provides
device control and
endpoint DLP across Windows, macOS, and Linux, deployable as hardware appliance, virtual appliance, or cloud instance with lightweight agents. It features granular USB control and content-aware protection. Best fit: teams with heavy removable-media risk across mixed operating systems. Limitation: it’s primarily focused on endpoint-level enforcement rather than deep network traffic inspection.
Netwrix: Data Access Governance Plus DLP
Netwrix identifies sensitive data and monitors user behavior, deployable fully on-premises or in the cloud with a centralized server and optional lightweight agents, including
data classification and Active Directory auditing. It provides deep coverage across on-premises repositories, including SMB/CIFS file shares, Active Directory, and on-premises databases, alongside its cloud-native capabilities. Best fit: teams that need data access governance and compliance reporting alongside DLP, including in on-premises-heavy environments. Limitation: teams should still confirm coverage of their specific cloud SaaS stack during evaluation, since access governance breadth varies by app.
Forcepoint: Unified Policy Across Cloud, Web, and Endpoint
Forcepoint provides enterprise DLP across endpoints, networks, and cloud apps with a hybrid architecture and optional network appliances for web and email inspection, plus AI-driven
data classification. Best fit: teams that already run a broader Forcepoint or SSE footprint and want unified policy management. Limitation: comprehensive on-premises deployment still requires managing servers and databases.
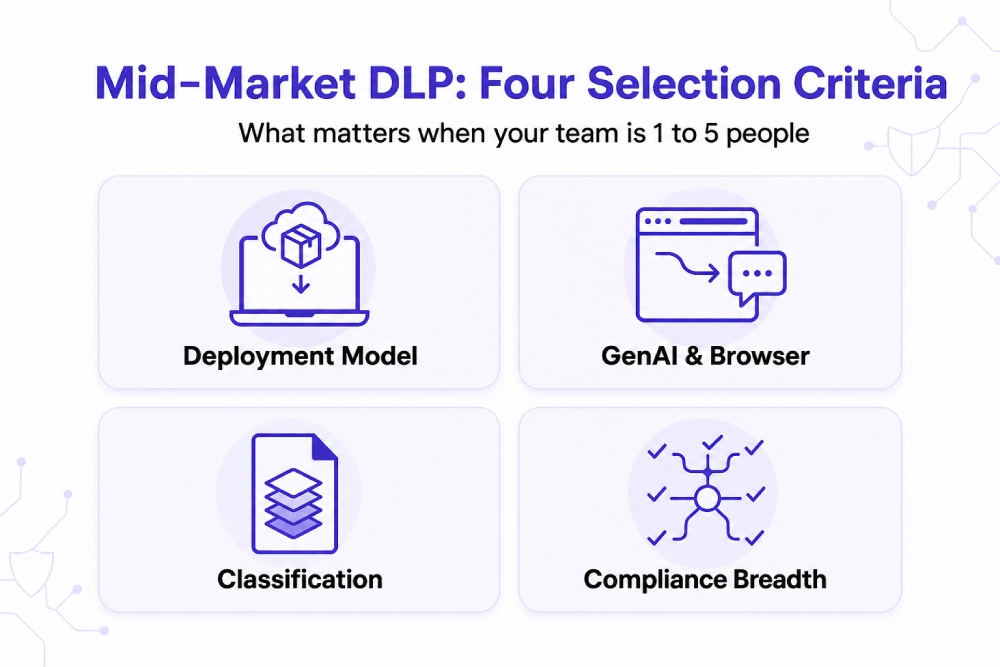
What Are the Four Selection Criteria That Actually Matter Here?
Narrowing seven platforms to one comes down to four factors, weighted for a small team.
|
Criterion
|
Why it matters at 250-1,000 employees
|
|
Deployment model
|
An agent-based, cloud-managed rollout gets to production in days; appliance-dependent architectures add hardware and patching work a small team doesn’t have time for.
|
|
GenAI and browser coverage
|
If the tool can’t see data pasted and uploaded into AI tools and clipboard-level activity, it misses the exfiltration path employees actually use today.
|
|
Classification accuracy
|
Context-aware classification (document context, not just regex) reduces the false-positive volume a one-to-five-person team has to triage by hand.
|
|
Compliance breadth per agent
|
A platform that closes more audit gaps from a single agent prevents additional procurement cycles.
|
DLP pricing varies by vendor and tier, and none of it should be assumed without a quote, but the deployment and staffing cost behind the sticker price is often the bigger factor at this headcount.
Each platform above fits a different priority. Kitecyber suits teams that want a single lightweight agent covering both traditional DLP and GenAI paste/upload activity without a second deployment, though buyers with highly specific SaaS stacks should validate coverage in a trial. Safetica fits teams that want straightforward endpoint and cloud DLP without appliance overhead, though document-heavy environments should test its OCR against real scanned files. Nightfall fits teams whose main exposure is SaaS and GenAI sprawl, though its cloud dependency means connectivity issues can affect detection. Cyberhaven fits teams that most need to trace how a file moved and changed hands, though its value depends on full agent or extension deployment across the fleet. Endpoint Protector fits teams with heavy removable-media risk across mixed operating systems, though it leans more toward endpoint enforcement than deep network inspection. Netwrix fits teams that want data access governance alongside DLP, including strong on-premises repository coverage, though buyers should confirm coverage of their specific cloud SaaS stack during evaluation. Forcepoint fits teams already standardized on a broader Forcepoint or SSE footprint, though a fully on-premises deployment still means managing servers and databases.
About Kitecyber
Kitecyber is a data loss prevention company built for the GenAI era, delivering endpoint-native DLP through one lightweight agent that covers Windows, macOS, and native Linux devices, browser, email, clipboard, SaaS/cloud apps, and removable media. Its platform is designed specifically for the deployment realities of 250 to 1,000 employee security teams: fast setup, context-aware classification that cuts false-positive triage, and real-time enforcement at the exact point of risk.
See verified customer reviews of Kitecyber on G2 and SourceForge.
References
Frequently Asked Questions