Patch fast, then assume something got through
When the PHP project shipped emergency releases for two critical request-handling flaws (tracked as PHP2Shell) on 21 October, the response from security vendors was immediate. CrowdStrike and SentinelOne both published customer protection guidance within the day. Two days later, Unit 42 updated its analysis with something more unsettling: evidence that at least one intrusion was carried forward by an attacker whose behaviour it associates with an autonomous AI agent, and that attackers were using agentic AI attack platforms for post-exploitation.
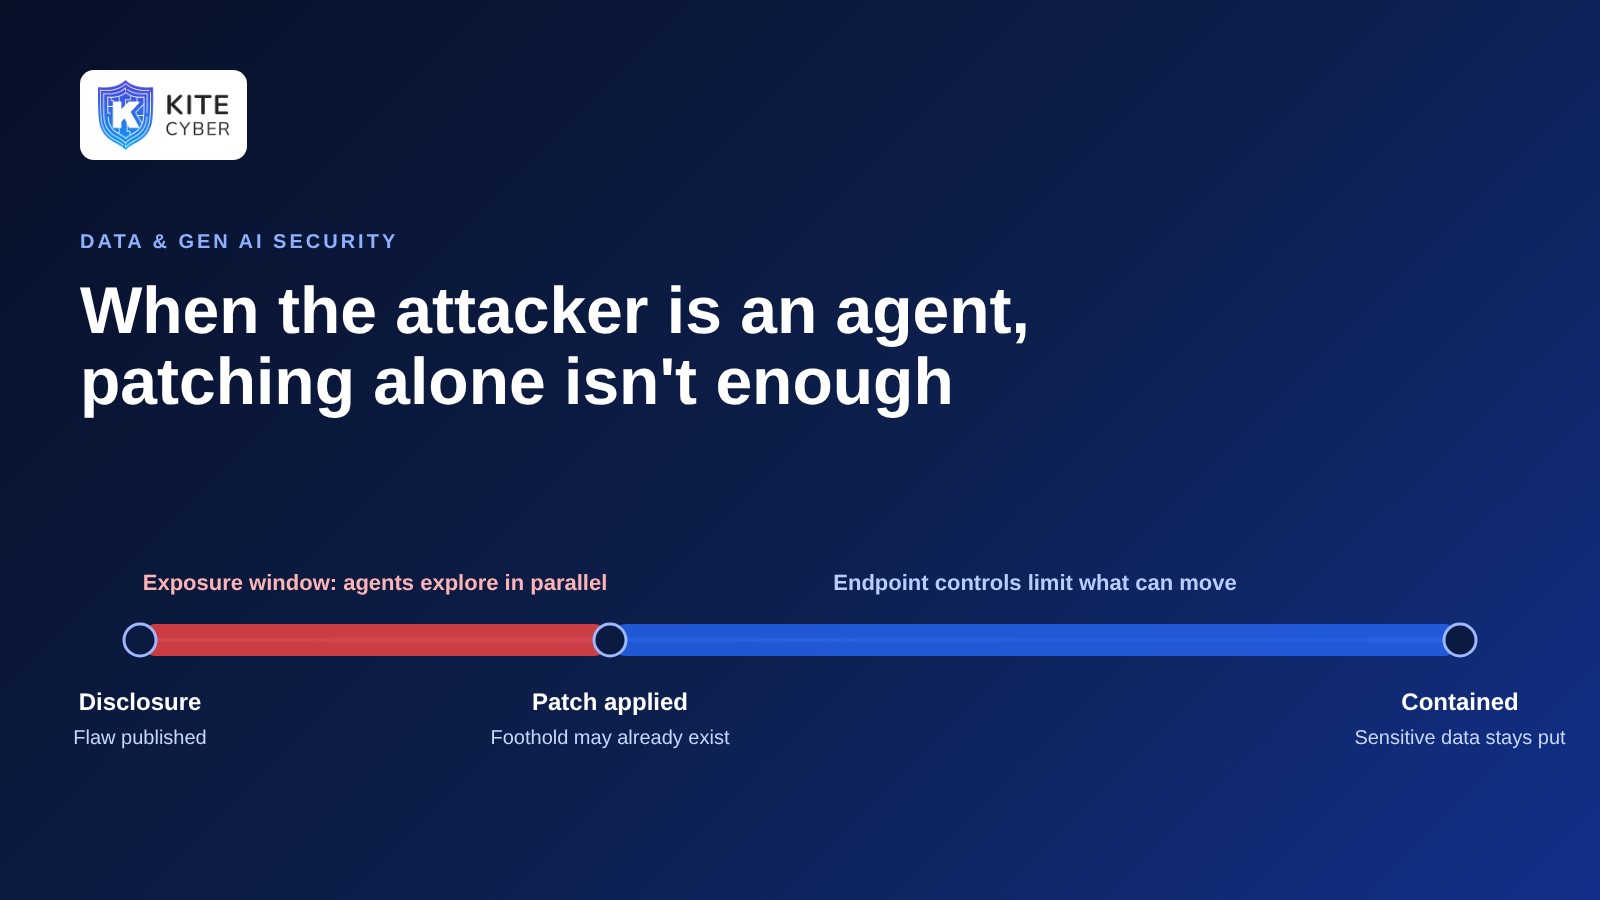
Patching remains step one. But the interesting detail is what happens in the gap between disclosure and patch, and what an agent does once it has a foothold.
Why agents change the arithmetic
A human operator with a new foothold has to look around, decide, and type. An agent explores in parallel, retries when something fails, and chains steps without waiting for a shift change. Zscaler and CrowdStrike have both described attacker tooling built from coding agents, reusable skills and MCP servers earlier this month. The practical effect is a shorter path from “code execution” to “data found and moved”.
That compresses the time defenders have to patch, triage and respond, which is why many teams are moving from “patch everything quickly” to “assume the first control may be late, and limit what can happen next.”
Post-exploitation looks familiar: enumerate the host, find credentials and configuration files, read source code and documents, and stage data for transfer. What differs is the volume and speed, and the fact that the activity can look like ordinary scripted tooling.
Notably, much of it happens on a device or server, in process and file activity, before any network control sees a byte. Network inspection is essential, but it sees the transfer, not the search that preceded it.
Containing the blast radius on the device
Keep it proportionate
None of this replaces patching, EDR or network controls. It adds a layer that limits the damage when those controls are late or bypassed, and it works best when alerts are tuned to risky combinations, such as sensitive data plus a new destination, rather than every file read.
Where Kitecyber fits
Kitecyber’s endpoint agent (under 2% CPU) combines device posture, process, file, user and network activity with data classification across 80+ categories. That context lets teams enforce policy on sensitive data movement from the device itself and keep an audit trail of what happened. Deployment typically takes around a day with pre-built compliance policies.
Book a Kitecyber walkthrough at kitecyber.com to see how endpoint data controls limit the blast radius while patches land.