Table of Content
When Employees Leave, Does Your Data Stay? Stopping Departing-Employee Data Loss in the AI Era
-
November 13, 2026
-
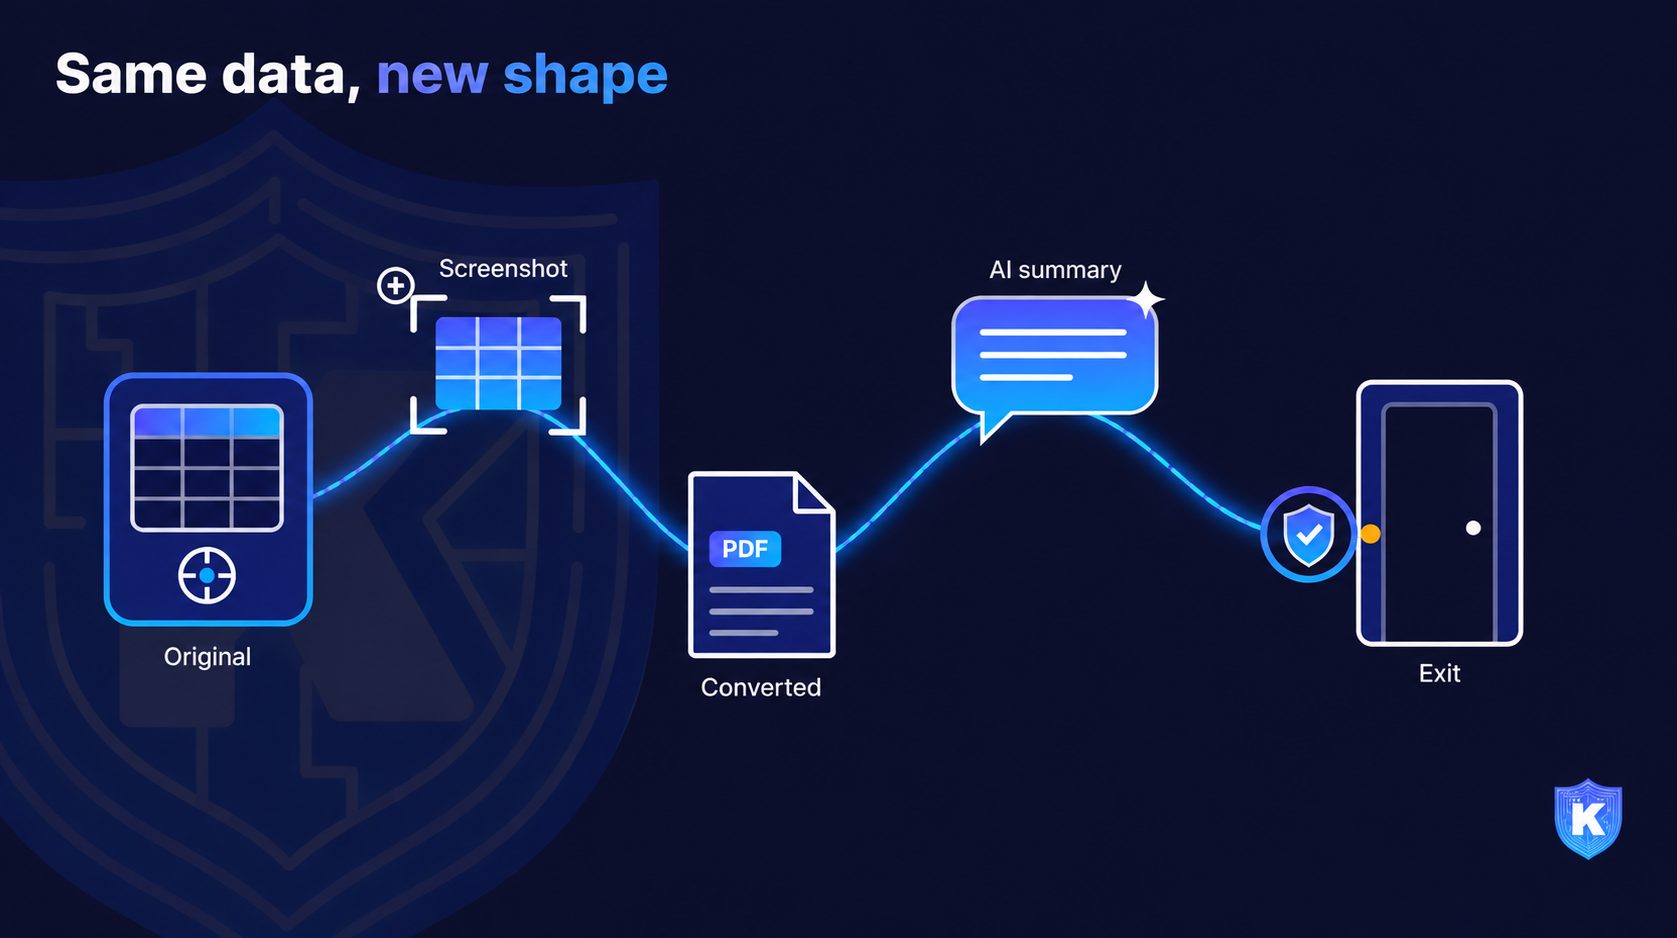
Sensitive data rarely leaves in its original form. It leaves as a screenshot, a converted PDF, a pasted excerpt or an AI-written summary, and most data protection tools stop recognizing it the moment it changes shape. This guide explains how data lineage lets small and mid-size security teams keep control of sensitive data through every copy and conversion, without drowning in alerts.
Same data, five different shapes
The following scenario is illustrative. The company and people are fictional.
A 1,200-person medical device maker keeps its next-generation pricing model in a spreadsheet on a restricted SharePoint site. The company’s DLP tool has a rule for it: the file can’t be emailed outside the company or uploaded to personal cloud storage.
A sales director, Daniel, is two weeks from joining a competitor. He doesn’t try to email the file. He opens it, takes six screenshots, and drops them into a slide deck. He exports the deck as a PDF and renames it “Q3 territory notes.” Then he pastes the key rows into an AI assistant and asks for “a one-page summary of discount tiers by region.” The summary goes into a personal notes app.
Every step looks like ordinary work. The rule that protected the spreadsheet never fires, because nothing that leaves is the spreadsheet. The pricing model walks out anyway, in five new shapes.
The problem: protection that stops at the first copy
Most data protection is built around files and patterns. It asks, “Is this the protected file?” or “Does this text contain a card number?” When data is screenshotted, converted, re-encoded, summarized or pasted into a new document, both questions return “no.” The sensitive content leaves, and nothing records where it came from.
The stakes are high. The IBM Cost of a Data Breach Report 2026 put the global average cost of a breach at a record USD 4.99 million, with a mean of 247 days to identify and contain one. Customer PII was the most commonly stolen or compromised data type, in 52% of breaches. Intellectual property appeared in nearly a third (32%) and was the costliest per record, at USD 196. IBM also found that breaches involving data stored across multiple locations took the longest to identify and contain, at 256 days. Scattered copies are slow to find and slow to fix.
The Verizon 2026 Data Breach Investigations Report adds a telling detail. In its DLP data, images were the second most common type of data submitted to external Gen AI tools, after source code. Screenshots are now a routine part of how data moves.
For an SME, this hits three places at once: customer data that triggers notification duties, trade secrets that can’t be recovered, and investigations that drag on because nobody can say where a document went.
How Gen AI changed it
Reshaping data used to take effort. Now it takes one prompt.
- Summaries and rewrites erase fingerprints. An AI assistant can turn a 40-page contract into a one-page brief, or a customer table into prose. The output carries the same secrets but matches none of the original text.
- Screenshots are AI input. Modern assistants read images as easily as text, so a screenshot of a dashboard is as useful to an outsider as the export.
- Copies multiply quietly. Every prompt, response and AI-generated draft is a new copy, often stored in chat histories outside company control.
- Agents move data between tools. AI agents and copilots can read a folder, convert files and post the results elsewhere under an employee's session, faster than anyone reviews.
- Attackers move faster too. IBM found AI-driven attacks rose 56% in a year and added an average of USD 1 million to the cost of a malicious breach. Once data is out, it gets used quickly.
Why legacy approaches fall short
- Pattern-based (regex) DLP only recognizes data that looks like a known format. A pricing table in a screenshot, a summary in plain English or a Base64-encoded file slips past, while harmless text with the wrong digits fires false alarms.
- File-label and fingerprint controls protect the original file. They lose the trail when content is copied into a new document, exported to another format or renamed.
- Network-only and cloud-proxy inspection sees what crosses the gateway. It can't see a screenshot taken on the laptop, a paste into a desktop app or a file copied to USB, and it misses traffic from devices off the corporate network.
- Block-everything rules on file types or apps stop real work and push people toward workarounds that are even harder to see.
- Heavy investigation suites can reconstruct a trail after the fact, but they need analysts to stitch logs together for days. Lean teams need the trail recorded as it happens.
What a modern approach looks like
The answer is data lineage: a running record of where sensitive data came from, how it was changed and who or what touched it. With lineage, the question shifts from “Is this the protected file?” to “Did this content come from something sensitive?”
- 1.Know the origin. Classify sensitive data where it is created and stored, so every later copy inherits that context.
- 2.Follow the content, not the file name. Keep the link when data is screenshotted, encoded, converted, renamed or pasted into a new document.
- 3.Watch both people and AI. Record actions by employees, AI assistants and agents in the same trail.
- 4.Decide with context. A sales deck going to a customer is normal. The same deck built from restricted pricing data and headed to a personal account is not.
- 5.Keep the evidence. A clean chain of custody turns a week-long investigation into a short review.
This is where analyst and government guidance points. Forrester’s Heidi Shey writes that agentic AI amplifies existing weaknesses, including “unclear classification” and “incomplete lineage.” Gartner’s 2026 cybersecurity predictions say that through 2030, one-third of the work in IT will be spent remediating “AI data debt” to secure AI. And joint guidance from CISA, NSA, FBI and international partners on AI data security recommends tracking data provenance so organizations can trace where data originated and the path it followed.
How Kitecyber helps
Kitecyber’s Data Shield applies lineage on the endpoint, the one place that sees every screenshot, conversion, paste and upload as it happens. One lightweight agent and one console cover data security, Gen AI security, web security, zero-trust access and device management.
- Data lineage through transformation. Kitecyber tracks sensitive data when it is screenshotted, encoded or converted, so a customer-records spreadsheet stays governed after it is reshaped. Its site describes lineage tracking across devices, email, SaaS applications and networks in real time.
- Classification that understands content. Hybrid LLM and on-device classification covers 80+ data categories, including PII, PHI, PCI data, IP and source code, with 90%+ classification accuracy. Sensitive content stays on the device.
- Discovery at rest. Find and classify sensitive data already sitting on laptops, so you know the origin before anything moves.
- Enforcement on every exit. Allow, warn or block at the moment of action across browsers and installed apps, USB, network drives, cloud storage, local file sharing, SaaS uploads, real-time copy and paste, Gen AI prompts and uploads, and collaboration apps such as Teams, Zoom and Slack. Policies keep working offline.
- Context for investigations.UEBA flags unusual behavior, and incident reports are generated in minutes when activity and sensitive data combine suspiciously, with no baseline to learn first.
What day one looks like. The agent deploys through your existing MDM or a self-service link in about a day, with under 2% CPU overhead and pre-built compliance policies. Start by discovering where your crown-jewel data lives: customer records, pricing, source code. Run lineage in monitor mode for a week to see how that data really moves. Then turn on warn or block for the riskiest paths, such as derived copies headed to personal cloud storage, USB or unsanctioned AI tools.
SME decision-maker checklist
- 1.Name your crown jewels. List the five data sets that would hurt most if they leaked, and where each one lives today.
- 2.Run the screenshot test. Ask any vendor to show what happens when someone screenshots a protected file and pastes the image into a chat app or AI tool.
- 3.Run the conversion test. Export a protected spreadsheet to PDF, rename it and copy it to USB. Does the control still know what it is?
- 4.Ask how classification works. Pattern matching alone will miss summaries and prose. Ask for accuracy on your own sample data.
- 5.Check the trail. Can the tool show, in one view, where a piece of data started and every place it went?
- 6.Count the people needed. Ask how many analyst hours a week the tool needs at your size. If the answer is "a full-time team," keep looking.
- 7.Test off-network. Repeat the tests from home Wi-Fi with the VPN off.
Compliance angle
Data taken by a departing employee isn’t only a competitive problem. It can be a reportable one.
| Framework | Why lineage matters |
|---|---|
| GDPR | Data subject requests and erasure require finding every copy of a person’s data, including derived ones. |
| HIPAA | PHI in any form, including images and summaries, must be safeguarded, and breaches must be assessed and reported. |
| PCI DSS | Cardholder data must stay within the defined environment, whatever its format. |
| SOC 2 | Confidentiality criteria expect controls over confidential information throughout its life. |
| ISO 27001 | Annex A controls on information classification, transfer and data leakage prevention apply to every copy. |
| CMMC | Controlled Unclassified Information must be protected wherever it flows, including copies on endpoints and removable media. |
Lineage also helps with evidence. When an auditor or customer asks where a data set went, a recorded chain of custody answers in minutes instead of weeks.
Key takeaways
- Sensitive data usually leaves in a new shape: a screenshot, a converted file, a pasted excerpt or an AI summary.
- File-based and pattern-only controls lose track after the first copy. Data lineage keeps the link between the original and every derivative.
- On-device lineage and classification let lean teams see the full trail and step in at the risky moment, without a full-time investigations team.
See the trail on your own data. Schedule a walkthrough at kitecyber.com to see how Kitecyber follows sensitive data through screenshots, conversions and AI tools on your own endpoints.
Ajay Gulati
Ajay Gulati is a passionate entrepreneur focused on bringing innovative products to market that solve real-world problems with high impact. He is highly skilled in building and leading effective software development teams, driving success through strong leadership and technical expertise. With deep knowledge across multiple domains, including virtualization, networking, storage, cloud environments, and on-premises systems, he excels in product development and troubleshooting. His experience spans global development environments, working across multiple geographies. As the co-founder of Kitecyber, he is dedicated to advancing AI-driven security solutions.