- The Kitecyber platform
A data security platform
that brought its own endpoint stack.
Kitecyber is endpoint-native DLP and Gen AI security. Device management, secure web gateway and zero trust access run in the same agent — not as a bundle, but because the data engine reads from them. You buy data protection. You get comprehensive endpoint coverage with it.
- One agent
- One policy engine
- One console
- No gateways or appliances

Trusted by Renowned Customers & Partners
- How it fits together
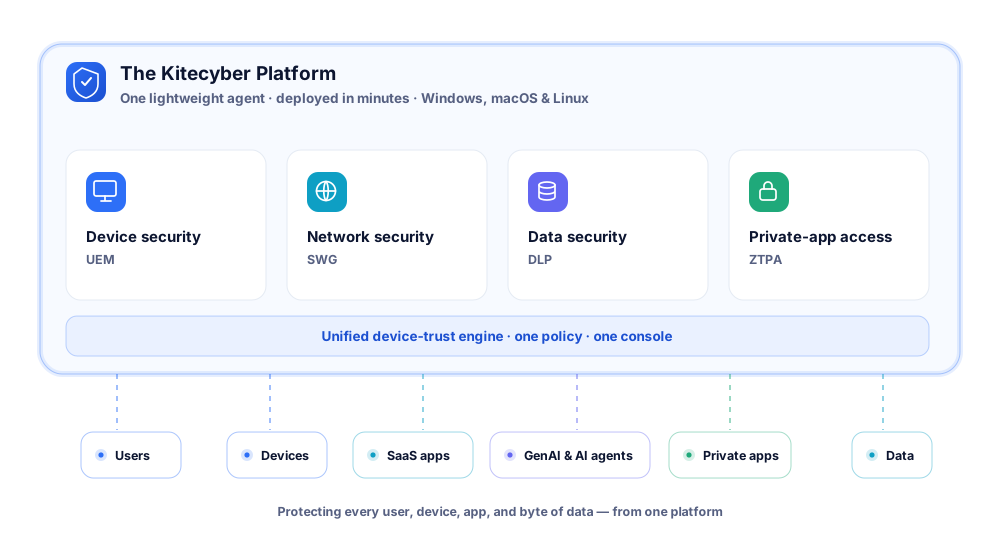
Two products at the core.
Three pillars underneath them.
Most stacks reach the data problem from one side and never get to the other. Data-first vendors build good classification engines and then have to guess at what the device was doing. Endpoint-first vendors have rich device telemetry and bolt pattern matching on top. Kitecyber runs the data engine inside the endpoint stack, which is why the classification is better and why the rest comes at no extra licensing.
- Core product
Endpoint and network DLP in one policy engine
Data Shield · DLP
Kitecyber discovers, classifies and protects sensitive data across endpoints, SaaS applications, email, network traffic and Gen AI tools — from one agent and one set of rules. Write the policy once; it applies on every channel, on or off the corporate network.
Contextual AI classification
80+ predefined categories — PII, PHI, PCI, intellectual property, source code — at over 90% accuracy, judged on what a document actually is rather than on regex, keyword lists or OCR alone.
At rest, in use, in motion
Continuous discovery across every managed device rather than a scheduled scan, so exposure surfaces when it appears instead of at the next crawl.
Lineage through transformation
Content stays governed after it is screenshotted, encoded, exported or converted into something a content scanner no longer recognises as sensitive.
Incident reports in minutes
Assembled automatically — what was touched, by which process, under which user, moving where — with no pre-built threat database and no historical baseline to learn first.
Insider risk signals
Unusual data movement, anomalous access patterns and policy violations surfaced with the device and process context that explains them.
Pre-built compliance packs
GDPR, SOC 2, HIPAA, PCI DSS, ISO 27001, FINRA and CMMC policies apply on day one, with audit evidence exported to GRC platforms including Scrut.
Every egress channel, one rule
- Data Shield · DLP
- AI Shield · Gen AI security
- Device Shield · UEM
- Web Shield · SWG
- Infra Shield · ZTNA
- CORE PRODUCT
Govern what AI tools and agents do with your data
AI Shield · Gen AI & agent security
Kitecyber discovers every Gen AI tool and AI agent reachable from a managed device, and detects, classifies and blocks sensitive data being pasted or uploaded into them before it leaves the endpoint.
Shadow AI discovery
Standalone tools such as ChatGPT, Claude, Gemini and Perplexity; AI features embedded inside SaaS applications; and third-party AI apps and agents connected to your SaaS through OAuth. Inventory first, policy second.
Paste and upload protection
Sensitive content is classified in the payload at the moment of the action, and the transfer is allowed, warned on, or blocked — before the data leaves the device, including on personal accounts a network proxy cannot distinguish by domain.
AI agent visibility
Which agents are running on the fleet, what skills they have loaded, what they connect to, and what privilege they inherited from the user they run as. Agent activity stops being invisible inside a human's session.
Coach, not only block
Warn-and-explain policies for the large share of AI usage that is careless rather than malicious, so employees stay productive instead of routing around the control on a personal device.
To be precise about what this is. Kitecyber tracks sensitive data pasted or uploaded into Gen AI tools. It does not read, inspect or log the full text of a user's prompt. The control is on the sensitive data in the payload, not on the contents of the conversation.
- Comprehensive coverage
Three pillars that make the data engine work — and replace three more vendors
These are not adjacent products bolted on for a bundle discount, and they are not a lighter version of the standalone tools they displace. They are full capabilities that happen to share an agent with the data engine — which is what lets every DLP decision be made with device, destination and access context already in hand.
SWG
Web Shield
A secure web gateway that runs on the endpoint instead of in a cloud proxy.
- URL and category filtering
- AI-driven phishing detection in real time
- Ransomware and malicious-content protection
- Browser isolation for risky destinations
- Geographic and network-based access controls
- Direct-to-internet performance, no traffic backhaul
What it gives the data engine: destination context and in-app visibility a cloud gateway cannot reach, because inspection happens on the device before the session is encrypted and shipped — so no bypass list, and no blind spot for certificate-pinned apps.
Commonly replaces: Zscaler Internet Access · Netskope · Cisco Umbrella · Sophos
UEM
Device Shield
Unified endpoint management and compliance across Windows, macOS and Linux.
- Device posture, patch state and disk encryption enforcement
- Configuration and policy baselines per group
- Zero-touch onboarding and offboarding
- Remote lock and wipe
- Continuous compliance evidence for audits
- Asset inventory across allocated and unallocated devices
What it gives the data engine: the difference between “a file was copied” and “a file was copied to removable media on an unencrypted device that failed its posture check ninety seconds earlier.”
Commonly replaces: Jamf · JumpCloud · Kandji · Intune · NinjaOne
ZTNA
Infra Shield
Zero trust private access that retires the legacy VPN.
- Passwordless, device-trust-based authentication
- Least-privilege, just-in-time subnet authorisation
- No inbound exposure of private applications
- Lateral movement contained by segmentation
- Full audit trail of every access path
- Access decisions that read live device posture
What it gives the data engine: the other half of the loop — not just where sensitive data went, but where it came from, and whether the session that pulled it should have had access at all.
Commonly replaces: Perimeter 81 · Tailscale · Twingate · Cisco AnyConnect
- Consolidation
What teams retire when they deploy this
Customers typically arrive running three to five of the following and leave running one agent. The saving is not only licensing — it is the policy drift between tools that no longer has anywhere to happen.
- A standalone endpoint DLP product
- A separate network DLP or CASB tier
- A cloud secure web gateway subscription
- A legacy VPN or a separate ZTNA vendor
- An MDM or UEM tool covering only one or two operating systems
- A shadow-IT or SaaS discovery point product
“Kitecyber helped us with IT, security and compliance as a unified solution. It saved us almost 50% in overall cost as compared to our previous solutions, while significantly improving our security and compliance. The built-in device management and IAM integrations also optimised our onboarding and offboarding workflows.”
Venkat Thiruvengadam
CEO, DuploCloud
“Kitecyber stood out as a single product that is able to replace multiple point solutions. We were looking for device management, compliance controls, SaaS security and VPN — it was very easy to install.”
Antony P.
DevOps and Security Lead — via G2
- Operations
What teams retire when they deploy this
Customers typically arrive running three to five of the following and leave running one agent. The saving is not only licensing — it is the policy drift between tools that no longer has anywhere to happen.
Operating systems
0
on one policy engine Windows, macOS and Linux, with the same enforcement on each.
To deploy across
~
0
day
a typical fleet with pre-built compliance policies live immediately.
CPU overhead
<
0
%
with no traffic backhaul and no latency penalty for the user.
No capability in the agent
0
tier
sits behind a licensing upgrade or an add-on SKU.
Deploys through what you have
Push the agent through your existing MDM or a self-service link. No gateway to stand up, no appliance to size, no device-enrollment prerequisite to clear first.
Integrates with your identity
Okta, Google Workspace and Microsoft Entra ID for user and group sync, so policy follows the org chart rather than a separate list you maintain by hand.
Feeds your GRC platform
Control evidence flows into GRC tooling including Scrut, so audit preparation stops being a quarterly screenshot exercise.
- Get started
See the whole stack in one console
Thirty minutes, your environment, your data. We will show you discovery, classification and enforcement running together with the device, web and access context behind them — and tell you plainly where we are not the right fit.
No credit card. All compliance frameworks supported. Free migration support.
Enforcement requires the agent, so unmanaged personal devices are outside its reach unless they are enrolled. Kitecyber is not an EDR, antivirus or network appliance, and it does not reach data at rest inside a SaaS application through an API the way a SaaS-native DLP tool does.
FAQ's
Frequently asked questions
Both, and the order matters. Data loss prevention and Gen AI security are the product — that is what Kitecyber is bought for and where the engineering depth sits. Device management, secure web gateway and zero trust access are included because the data engine reads from them: every classification decision is made with device posture, destination and access context already available. Buying the DLP means the endpoint stack comes with it.
Yes. Modules are licensed individually with discounts as more are added, and most customers start with two. The data engine works on its own, but its context advantage grows as more of the agent's capabilities are enabled — the UEM, SWG and ZTNA pillars are what supply the device, destination and access signals.
It is a full unified endpoint management capability: device posture and patch state, disk encryption enforcement, configuration baselines, zero-touch onboarding and offboarding, remote lock and wipe, and asset inventory across Windows, macOS and Linux. Customers routinely retire Jamf, JumpCloud or Intune when they deploy it. The same is true of the secure web gateway and the zero trust access layer.
Kitecyber delivers the capabilities an SSE platform provides — secure web gateway, zero trust network access and data protection — but enforces them on the endpoint instead of in a cloud service. There are no points of presence to route through, which removes the latency, application-compatibility and decryption trade-offs that come with a gateway architecture. The difference in practice is that there is no bypass list.
No. EDR and antivirus look for malicious code and anomalous execution. Kitecyber governs sensitive data and the users, applications and AI agents that touch it. The two are complementary and most customers run both.
No. Kitecyber classifies sensitive data in the paste or upload payload and can block the transfer before it leaves the device. It does not read, inspect or log the full text of a user's prompt.
Windows, macOS and Linux, with the same policy engine and the same enforcement on all three. Cross-platform parity matters here — several competing products document Windows and partial macOS support with no Linux endpoint client at all.
Enforcement requires the agent, so unmanaged personal devices are outside its reach unless they are enrolled. Kitecyber is not an EDR, antivirus or network appliance, and it does not reach data at rest inside a SaaS application through an API the way a SaaS-native DLP tool does. If those are your requirements, we will say so on the first call.