Static risk tiers assign an employee a fixed risk label (low, medium, high) based on role, tenure, or department, and then rarely update it until the next scheduled review. That model fails to catch the most damaging insider cases: the employee who was scored “low risk” for three years and then, following a resignation, a demotion, or a personal financial crisis, moved sensitive data out the door in a single afternoon. Traditional static risk scoring models rely on fixed attributes, predefined checklists, and periodic reviews, which limits their effectiveness against rapidly changing environments, emerging threat patterns, and sudden behavioral shifts in employees. The fix isn’t a better checklist. It’s continuous, behavior-based risk assessment that updates in real time as actions happen, not on a quarterly cadence.
TL;DR
About the Author: This article is published by Kitecyber. Kitecyber is a data security company that builds endpoint-native DLP and insider risk detection for organizations adopting GenAI and agentic AI tools. Kitecyber’s platform is used by security and IT teams at AI-native companies including DuploCloud, Vanta, and Scrut Automation to monitor data movement and insider risk continuously at the point where work happens: the endpoint.
What Is Insider Threat Scoring and Why Does It Exist?
Insider threat scoring is the practice of assigning a numerical or tiered risk value to individual employees based on access and behavior, with the goal of prioritizing monitoring and investigation resources with data security at the center: real-time detection of data exfiltration and unauthorized data movement through endpoint DLP and AI-agent security is the foundation, with network DLP and supporting controls providing additional visibility across the data flow. Insider risk itself is the potential for loss caused by people inside the organization, whether through malice, negligence, or accident. Security teams built scoring models because they can’t investigate every employee with equal intensity; someone has to triage.
The problem isn’t the concept of scoring. It’s how most programs implement it: a point-in-time snapshot rather than a running calculation. An employee gets scored during onboarding based on role and access level, maybe rescored annually or after a policy review, and otherwise sits untouched in whatever tier they were assigned. That’s a reasonable way to allocate audit hours. It’s a poor way to catch someone whose intent changes on a Tuesday.
Why Do Static Risk Tiers Miss Employees Who Turn Overnight?
Static tiers miss sudden turns because they measure who someone is, not what someone is doing right now. A tier built on job title, department, and years of tenure tells you almost nothing about a person’s state of mind this week. Traditional static risk scoring models rely on fixed attributes, predefined checklists, and periodic reviews, and that rigidity is precisely what causes them to struggle with sudden behavioral shifts in employees.
Think of it like a fire alarm that only checks the building once a month instead of continuously sensing smoke. A monthly inspection will eventually find a fire hazard that’s been building for weeks. It will do nothing for a fire that started an hour after the inspector left. Insider risk works the same way: the “low risk” engineer who resigns on Monday and downloads a competitor’s worth of source code on Wednesday will not show up in a scoring model that only recalculates during quarterly reviews.
A few structural reasons static tiers fail on sudden shifts:
When Are Employees Most Likely to Turn?
Employees are statistically most dangerous around the edges of their employment, not during the steady middle of their tenure. Security research indicates that a high risk of insider data theft surrounds employment transitions, particularly terminations and resignations, with malicious activity frequently occurring within the 30 to 60 days prior to an employee’s departure and the 30 to 60 days following termination. That’s not a coincidence; it lines up with when access privileges, financial incentive, and emotional stakes all peak simultaneously.
This is where the value of continuous risk assessment becomes concrete rather than theoretical. A scoring system that only recalculates quarterly will almost never align with a 30-to-60-day departure window. A system that recalculates on every meaningful action, resignation notice logged in HR systems, unusual after-hours file access, a sudden spike in SaaS downloads, has a real chance of catching the window while it’s still open.
|
Risk model type
|
Update frequency
|
Catches gradual risk build-up
|
Catches sudden overnight turns
|
|
Static tier (annual/quarterly review)
|
Periodic
|
Sometimes
|
Rarely
|
|
Rule-based alerting (threshold triggers)
|
Event-triggered, narrow scope
|
Sometimes
|
Sometimes
|
|
Continuous behavioral scoring
|
Real time, every action
|
Yes
|
Yes
|
How Do Insider Threat Indicators Change Once AI Agents Are in the Mix?
The list of insider threat indicators used to be fairly stable: unusual login times, large file downloads, access to systems outside someone’s role, repeated failed authentication attempts. Those indicators still matter, but AI copilots and autonomous agents have added a category legacy models never had to account for: machine-speed action taken on a person’s behalf.
AI agents can exfiltrate sensitive data at machine speed, stealing tens of thousands of records in seconds or milliseconds, while a human operating manually would take significantly longer to access even a fraction of that volume. That single fact breaks the assumption baked into most legacy data exfiltration detection tools: that there’s a meaningful window between “risky access begins” and “damage is done” during which a security team can intervene. When an insider prompts a GenAI tool to summarize and export a customer database, or configures an autonomous agent to pull and forward records as part of a routine workflow, the exfiltration and the damage happen in the same instant.
This is the core reason insider threat detection software has to move from periodic review to real-time enforcement at the point of risk. It’s not enough to detect that data left the building an hour later. The decision, allow, block, warn, or escalate, has to happen at the moment the prompt is submitted or the file is dragged into an upload window.
Modern extensions of established frameworks are starting to reflect this. NIST SP 800-207 (Zero Trust Architecture) and CISA’s Insider Threat Mitigation guidelines historically leaned on static access controls, but current interpretations increasingly incorporate real-time behavioral analytics to catch sudden anomalies rather than relying solely on predefined trust boundaries.
What Does Continuous Risk Assessment Actually Look Like in Practice?
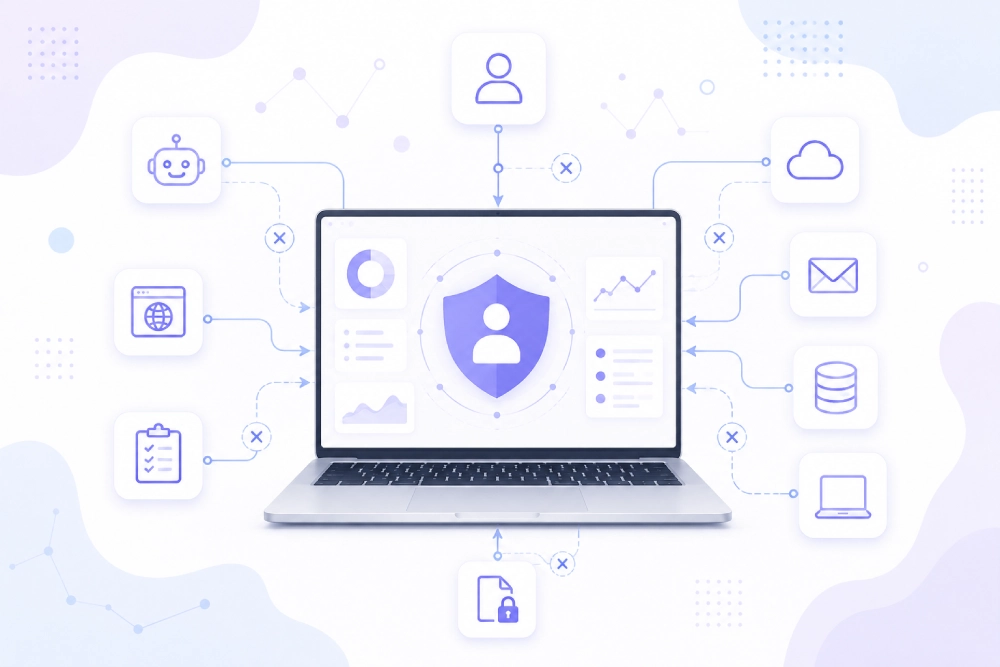
Continuous risk assessment means every meaningful action, an access request, a file download, a clipboard copy, a prompt submitted to a GenAI tool, an update to an autonomous agent’s task, feeds into a live risk calculation rather than sitting in a log for later review. Instead of a quarterly score, the employee has a running risk posture that shifts as their behavior shifts.
This is where Kitecyber’s operating model, See, Decide, Enforce, continuously, is built specifically for this problem rather than adapted to it. The endpoint agent observes activity across files, clipboard, browser uploads, GenAI prompts, SaaS apps, and removable media, evaluates each action against context (who is acting, what device, what data, where it’s headed), and enforces the appropriate control, allow, block, warn, coach, log, or isolate, at the moment the action occurs. Because the evaluation happens continuously rather than on a schedule, a resignation submitted Monday morning and an unusual bulk download Monday afternoon are connected in real time, not reconciled three weeks later during an incident review.
Kitecyber also tracks data lineage, meaning it can trace where a sensitive file has traveled and who or what has touched it, which matters enormously for insider cases where the damaging action isn’t a single dramatic download but a slow accumulation of small, individually unremarkable movements. Classifying data by document context, not just pattern matching, helps distinguish a legitimate customer-export workflow from the same action taken by someone whose behavioral pattern has just shifted.
What Should Security Teams Do Differently Starting Now?
Security teams should stop treating insider risk scoring as a static classification exercise and start treating it as a live signal that updates with every action. A few concrete practices follow from that shift:
About Kitecyber
Kitecyber is a data security company built for the era of AI agents, delivering endpoint-native DLP, insider risk detection, and GenAI security through one lightweight agent rather than a stack of disconnected point tools. The platform follows a continuous See, Decide, Enforce model, giving security and IT teams real-time visibility into data movement across files, clipboard, browser, SaaS apps, and autonomous AI agents. Kitecyber is used by AI-native and technology companies including D
Frequently Asked Questions